Create security groups
In this step we will proceed to create the security groups used for our instances. As you can see, these security groups will not need to open traditional ports for ssh such as port 22 or remote desktop through port 3389.
Create security group for Linux instance in public subnet
Access the VPC service management console
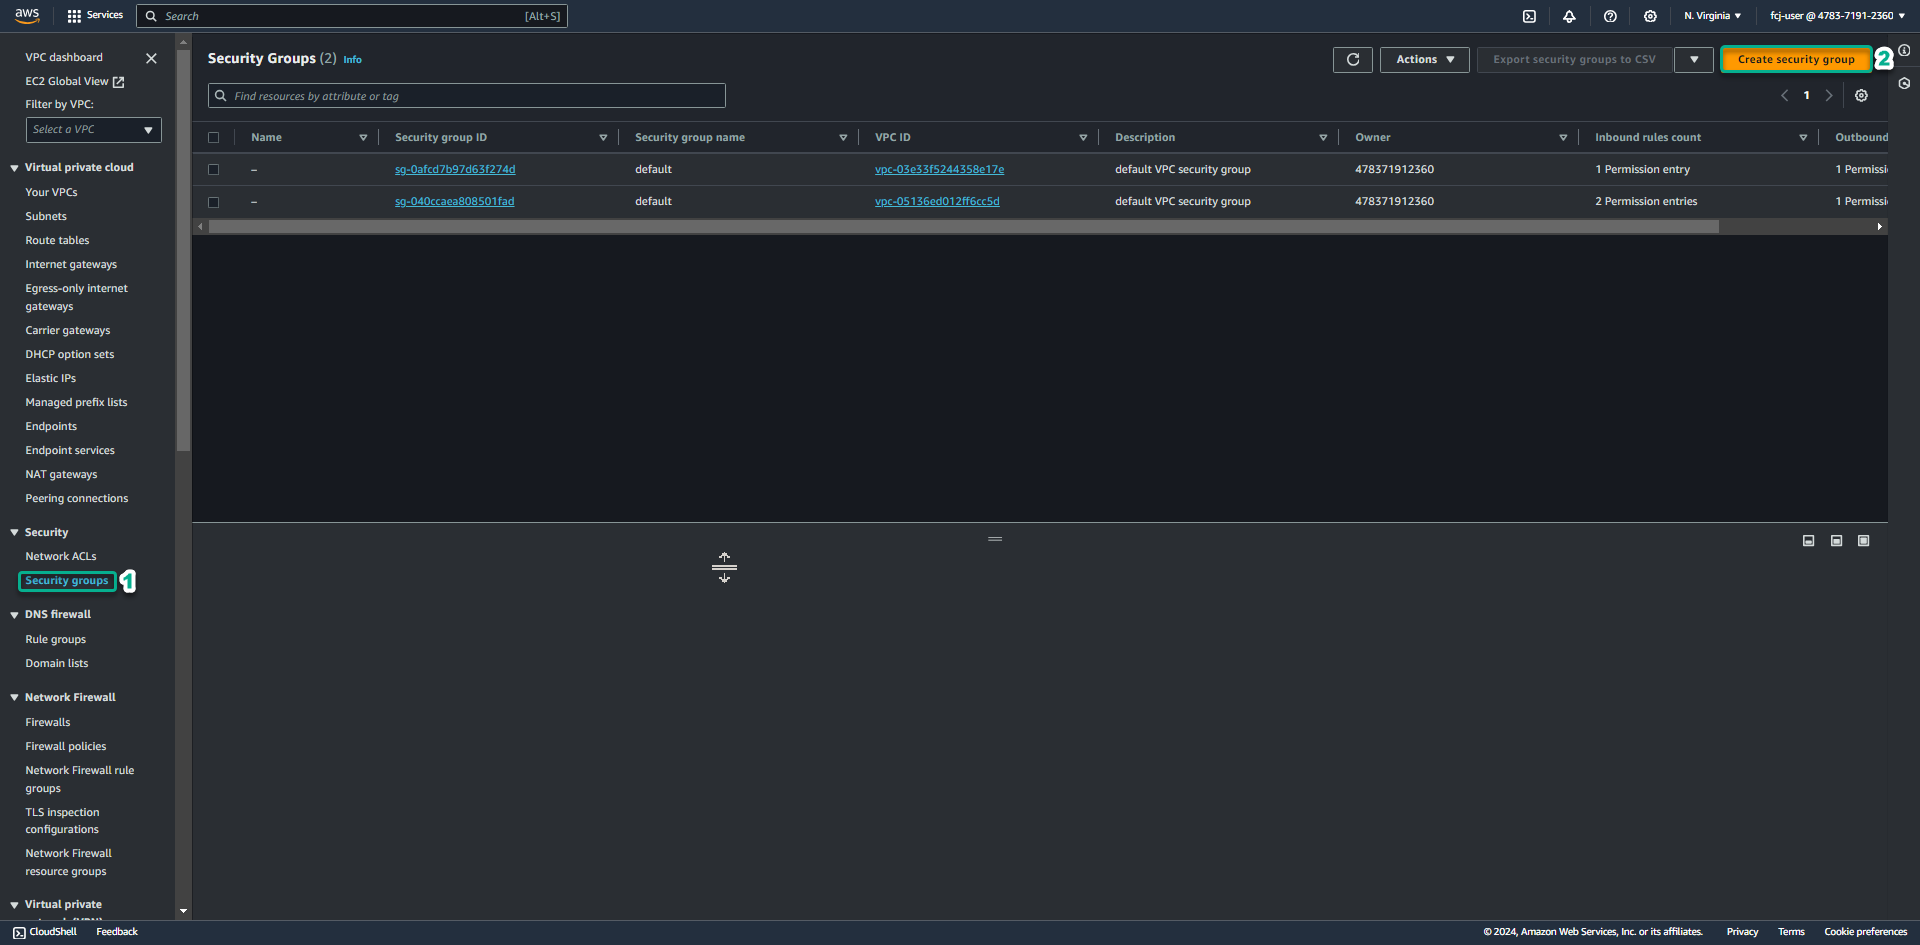
- Click Security Group.
- Click Create security group.
In the Security group name section, enter SG Public Linux Instance.
- In the Description section, enter SG Public Linux Instance.
- In the VPC section, click the X mark to reselect the Lab VPC you created for this lab.
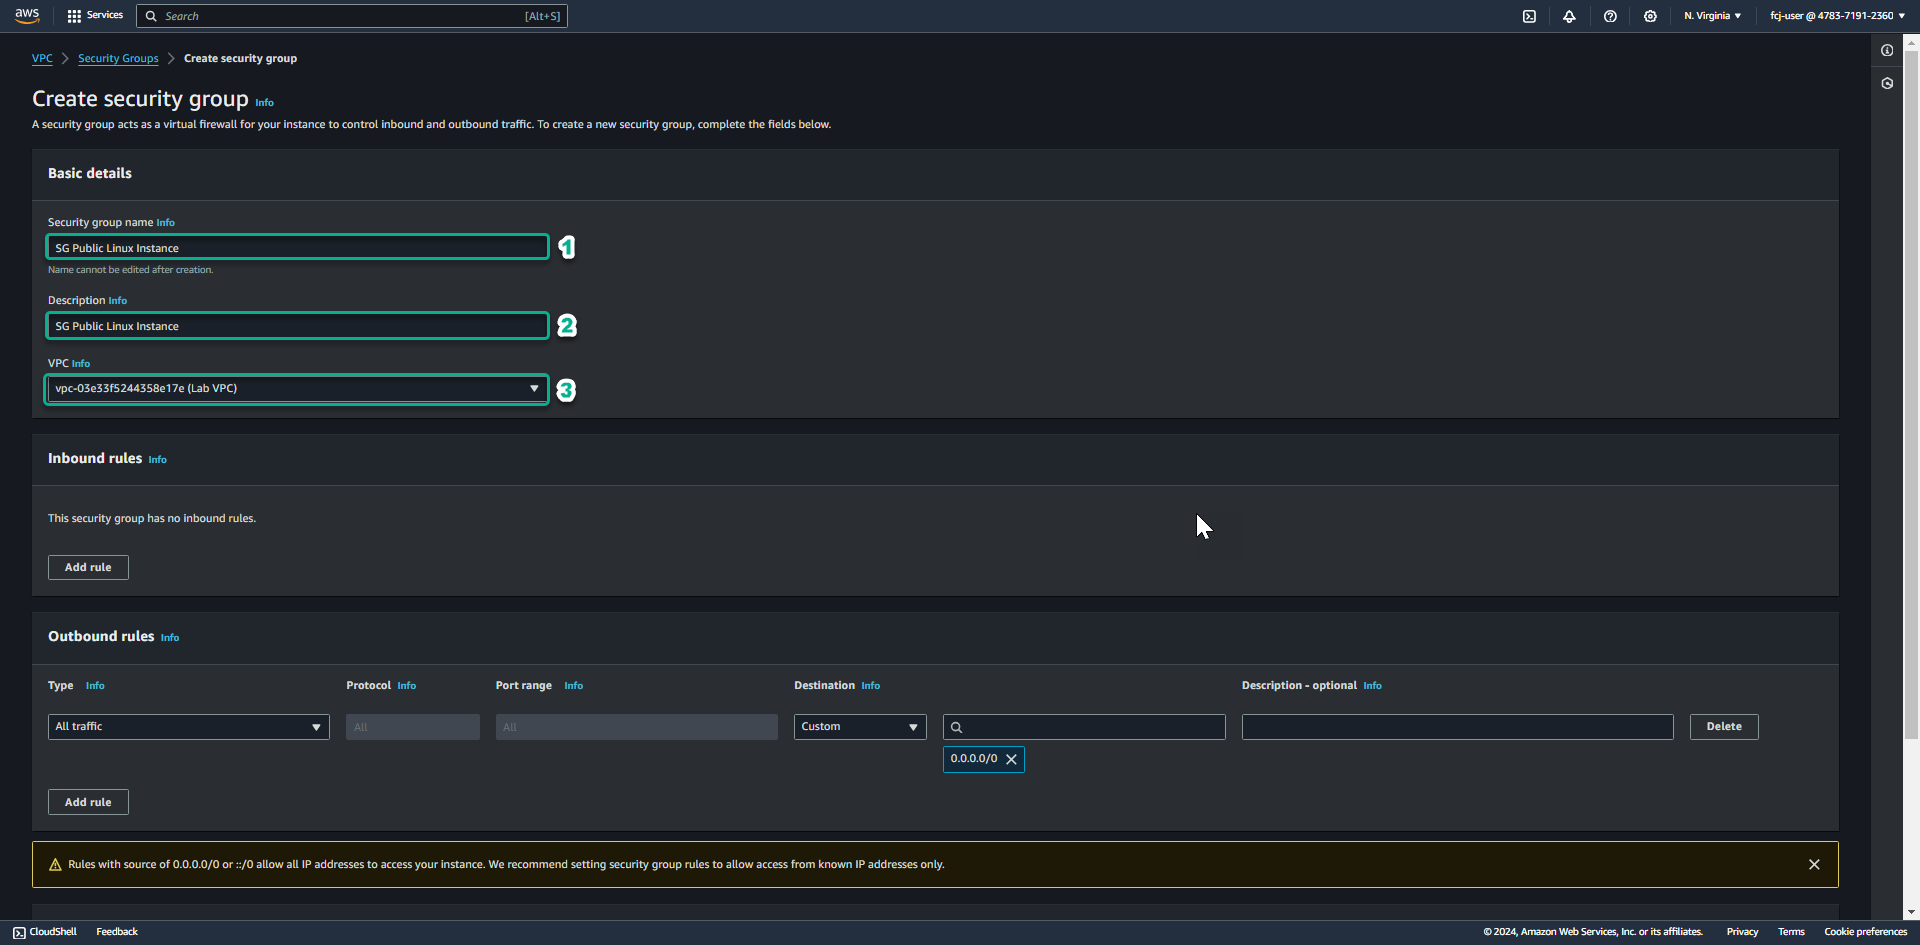
Keep the Outbound rule unchanged, scroll down.
- Click Create security group.
As you can see, the security group we create for the public Linux instance will not need to open traditional ports for ssh such as port 22.
Create security group for Windows instance in private subnet
After successfully creating the security group for the Linux instance in the public subnet, click the Security Groups link to return to the Security groups list.
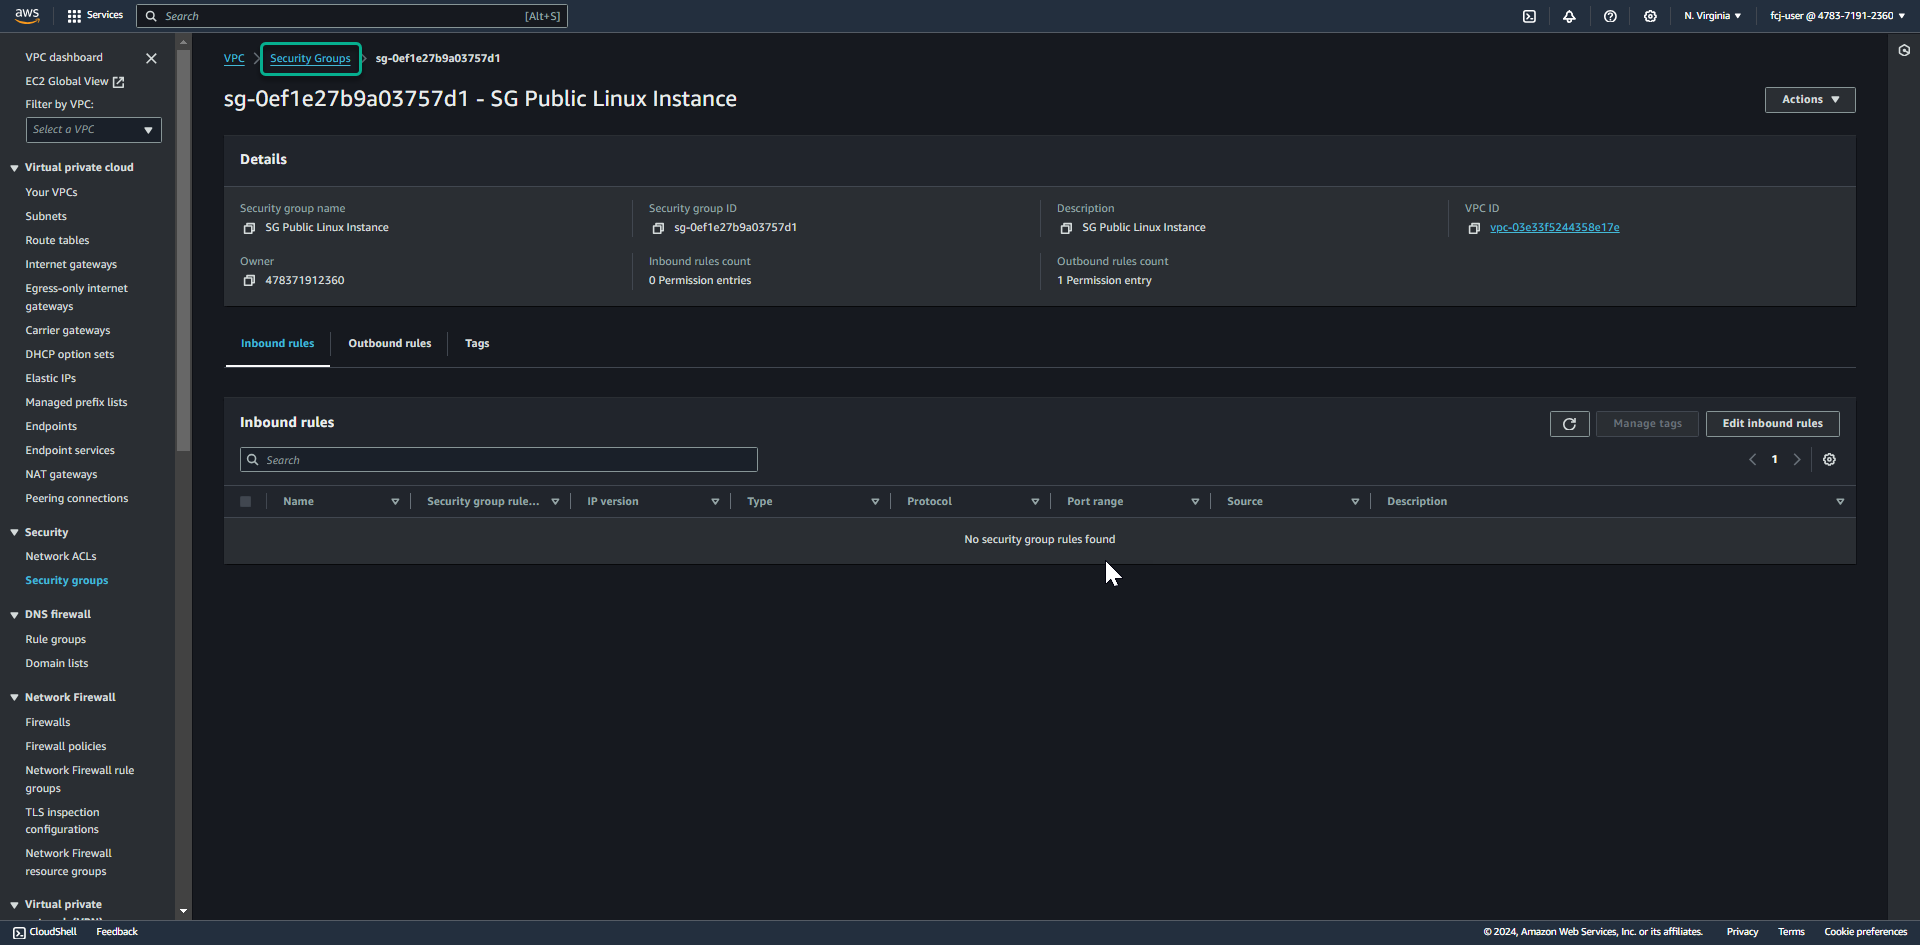
Click Create security group.
In the Security group name section, enter SG Private Windows Instance.
- In the Description section, enter SG Private Windows Instance.
- In the VPC section, click to reselect the Lab VPC you created for this lab.
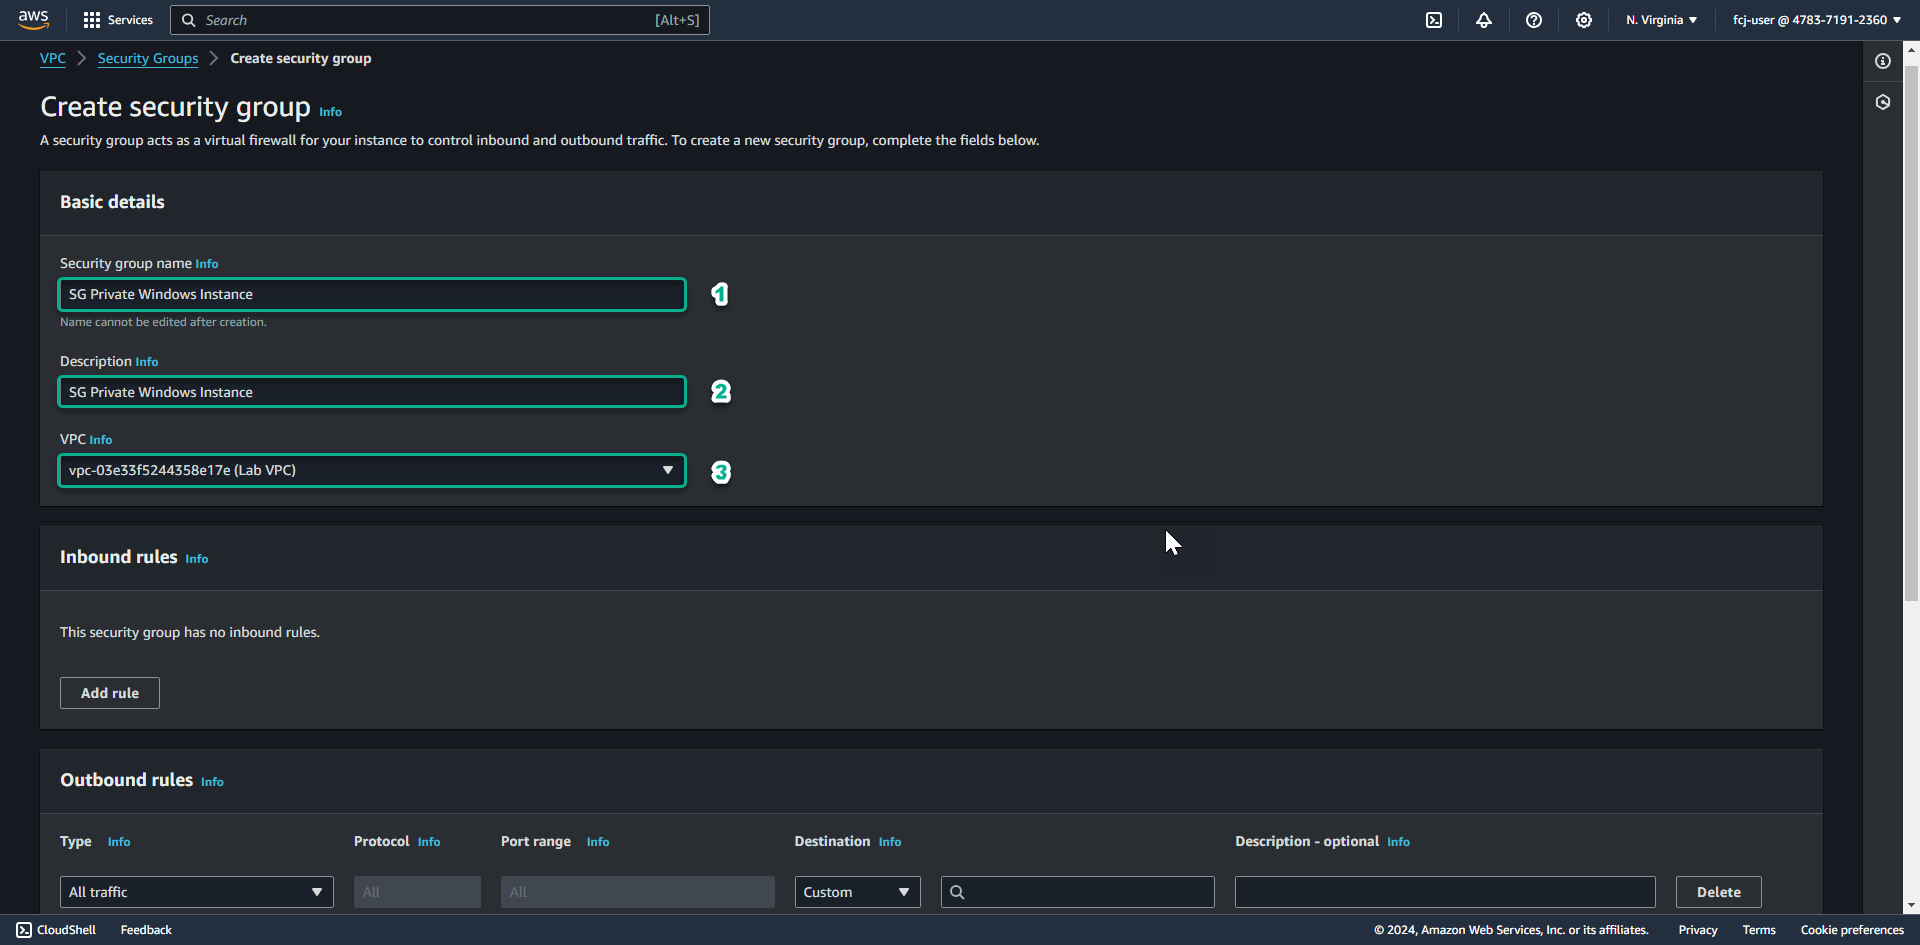
Scroll down.
- Add an Outbound rule to allow TCP 443 connection to 10.10.0.0/16 (CIDR of the Lab VPC we created)
- Click Create security group.
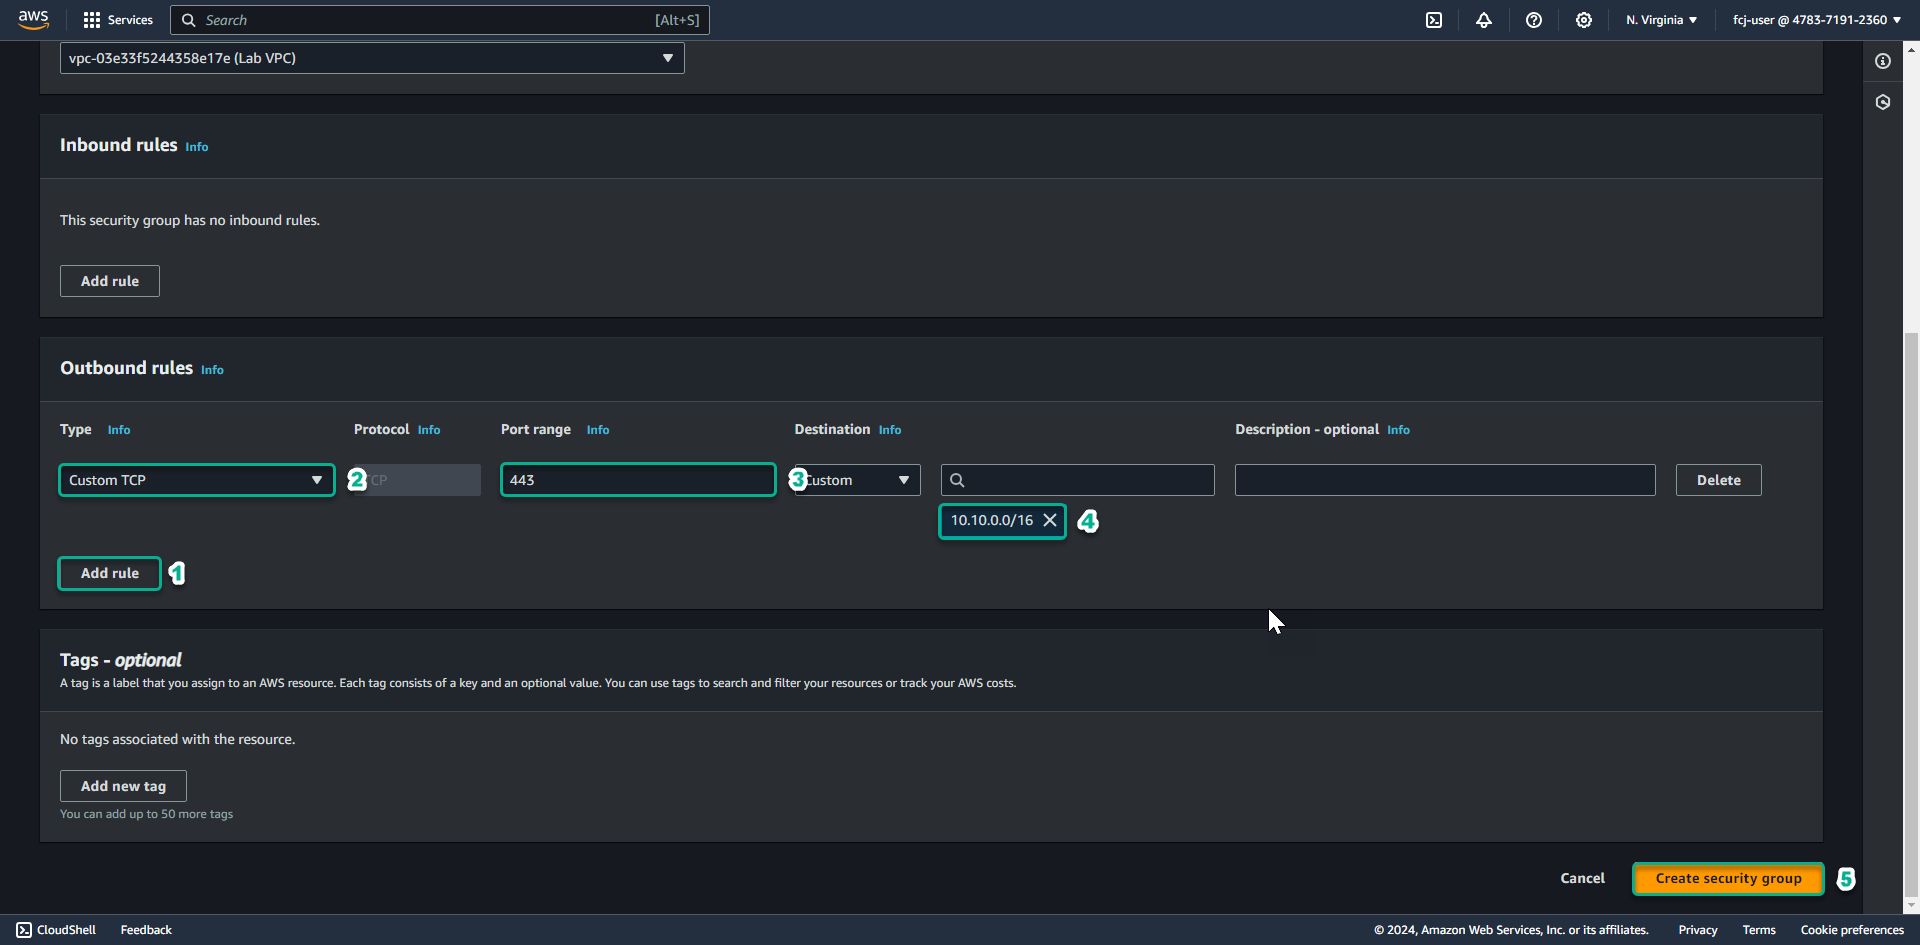
For Instances in a private subnet, we will connect to the endpoint of Session Manager through an encrypted TLS connection. Therefore, we need to allow outbound connections from our instance to the VPC CIDR through port 443.
Create security group for VPC Endpoint
In this step, we will create a security group for the VPC Endpoint of Session Manager.
After successfully creating the security group for the Windows instance in the private subnet, click the Security Groups link to return to the Security groups list.
Click Create security group.
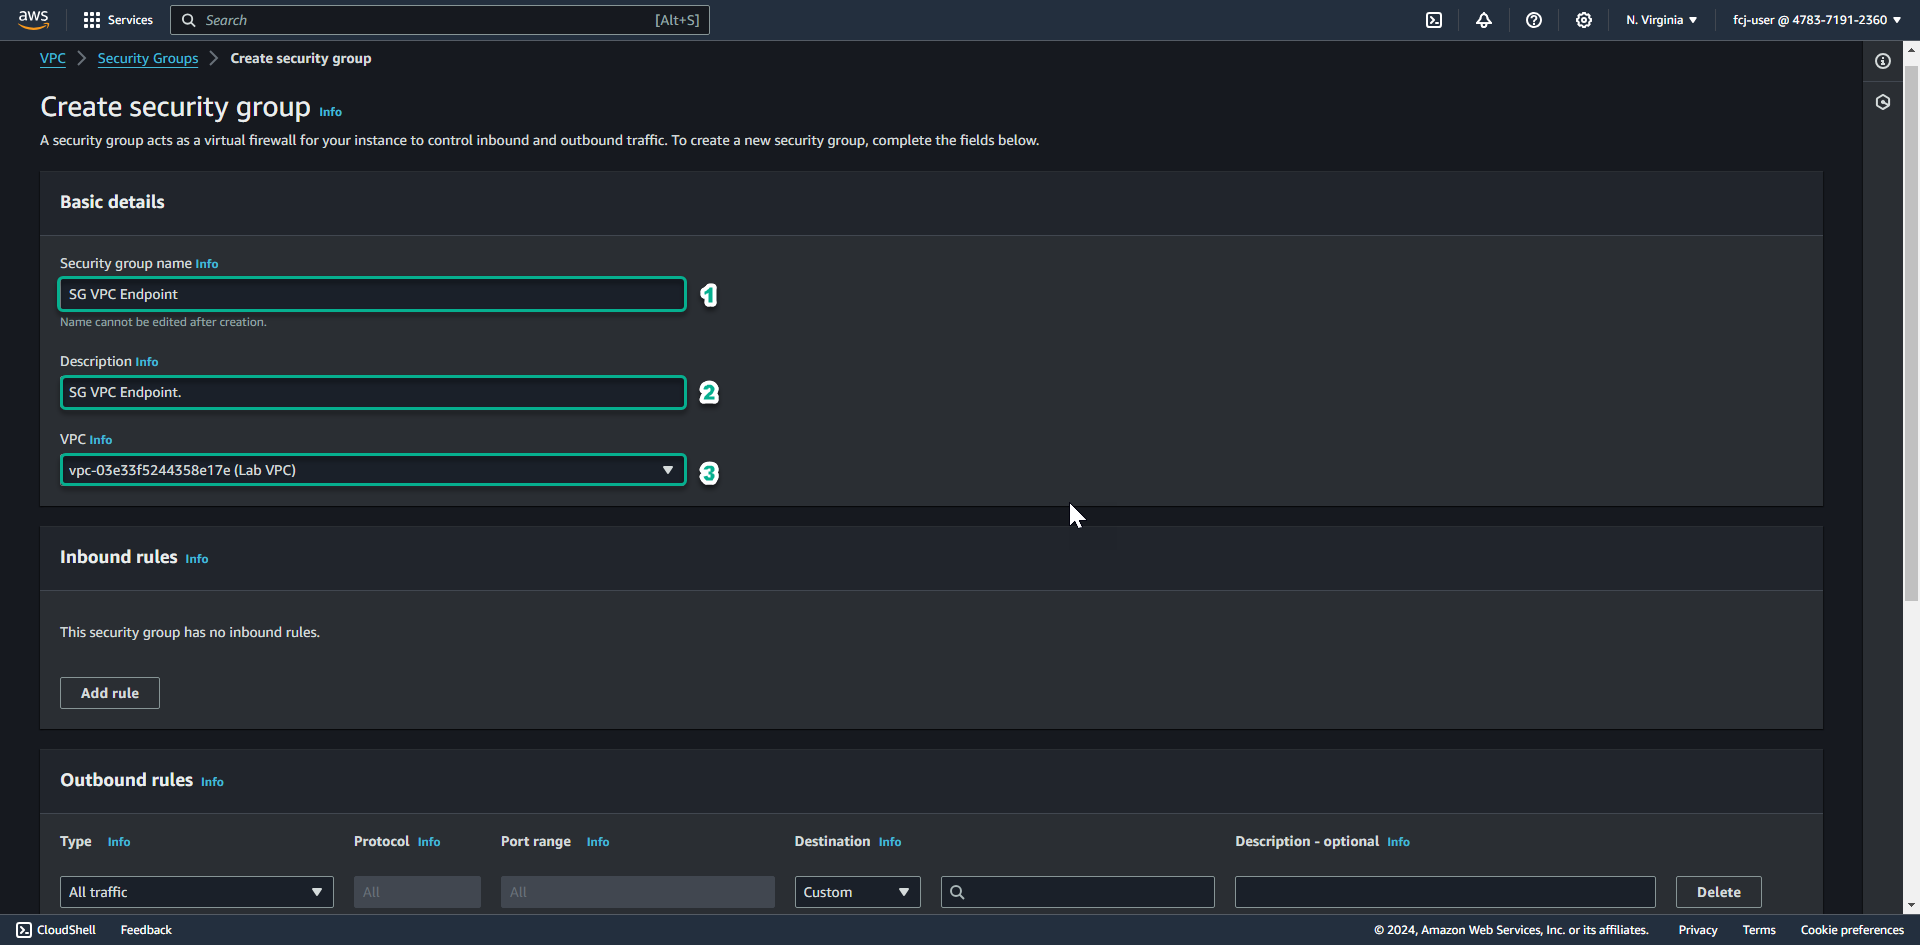
In the Security group name section, enter SG VPC Endpoint.
- In the Description section, enter SG VPC Endpoint.
- In the VPC section, click to reselect the Lab VPC you created for this lab.
Scroll down.
- Delete the Outbound rule.
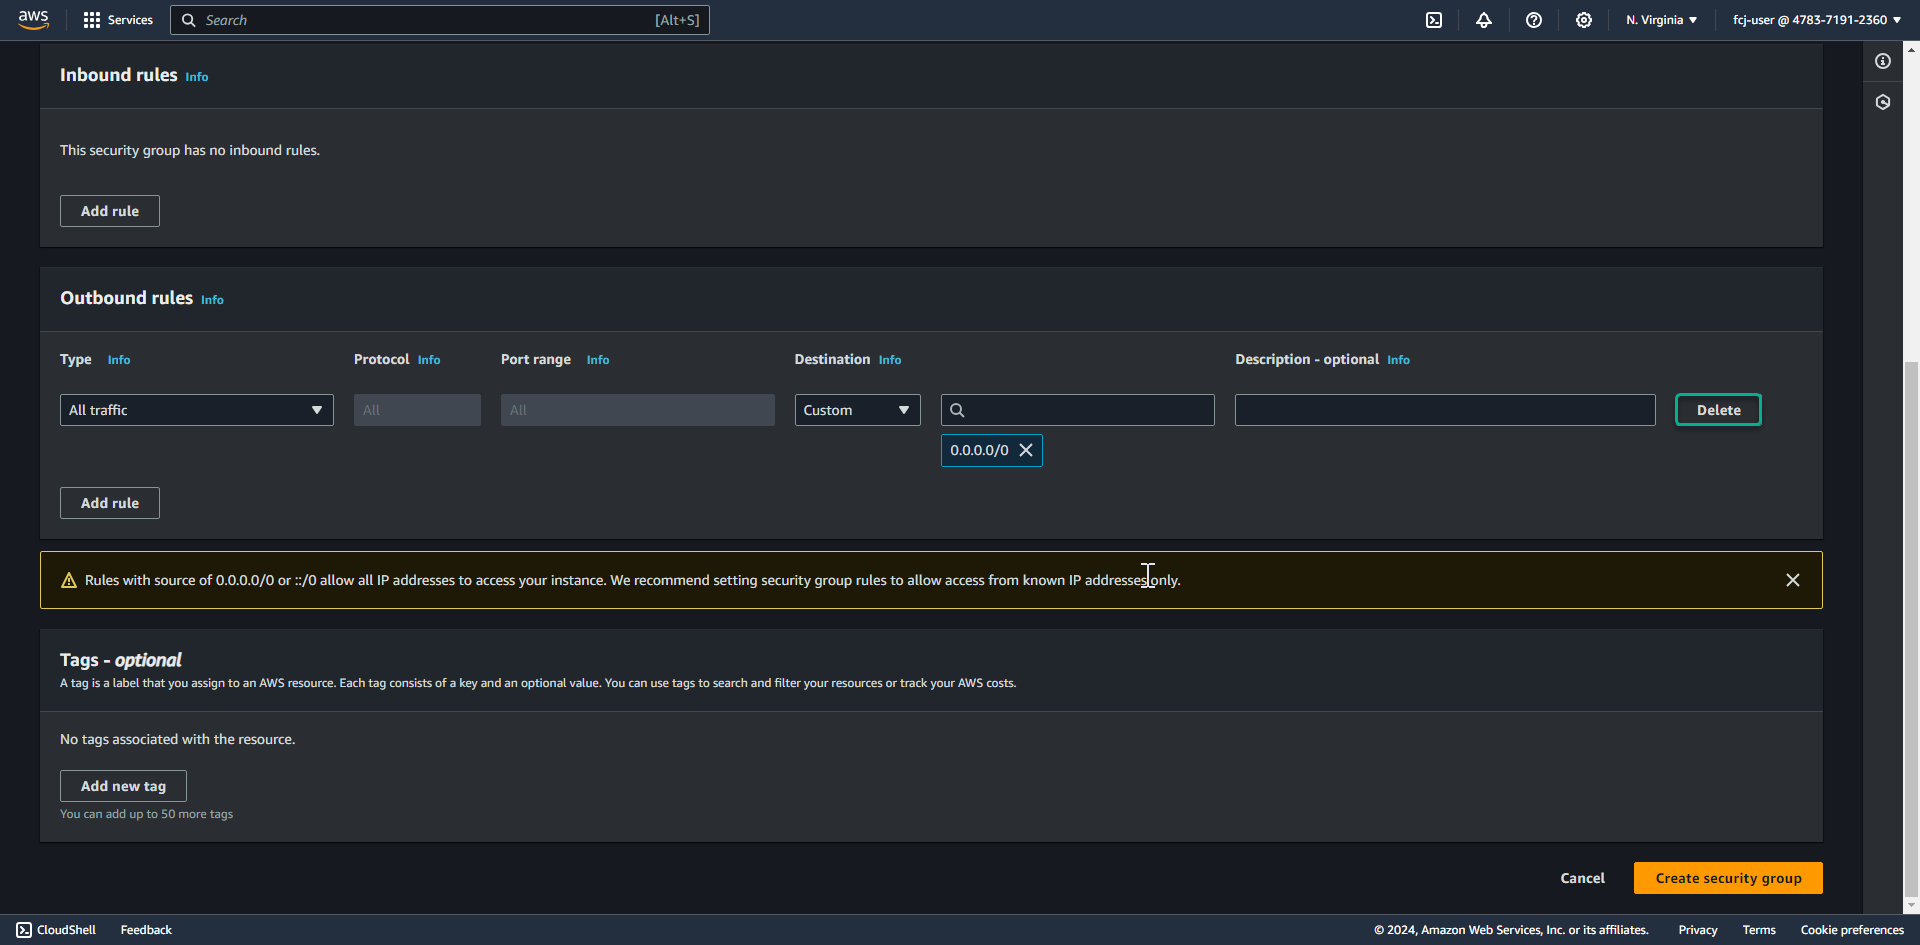
- Delete the Outbound rule.
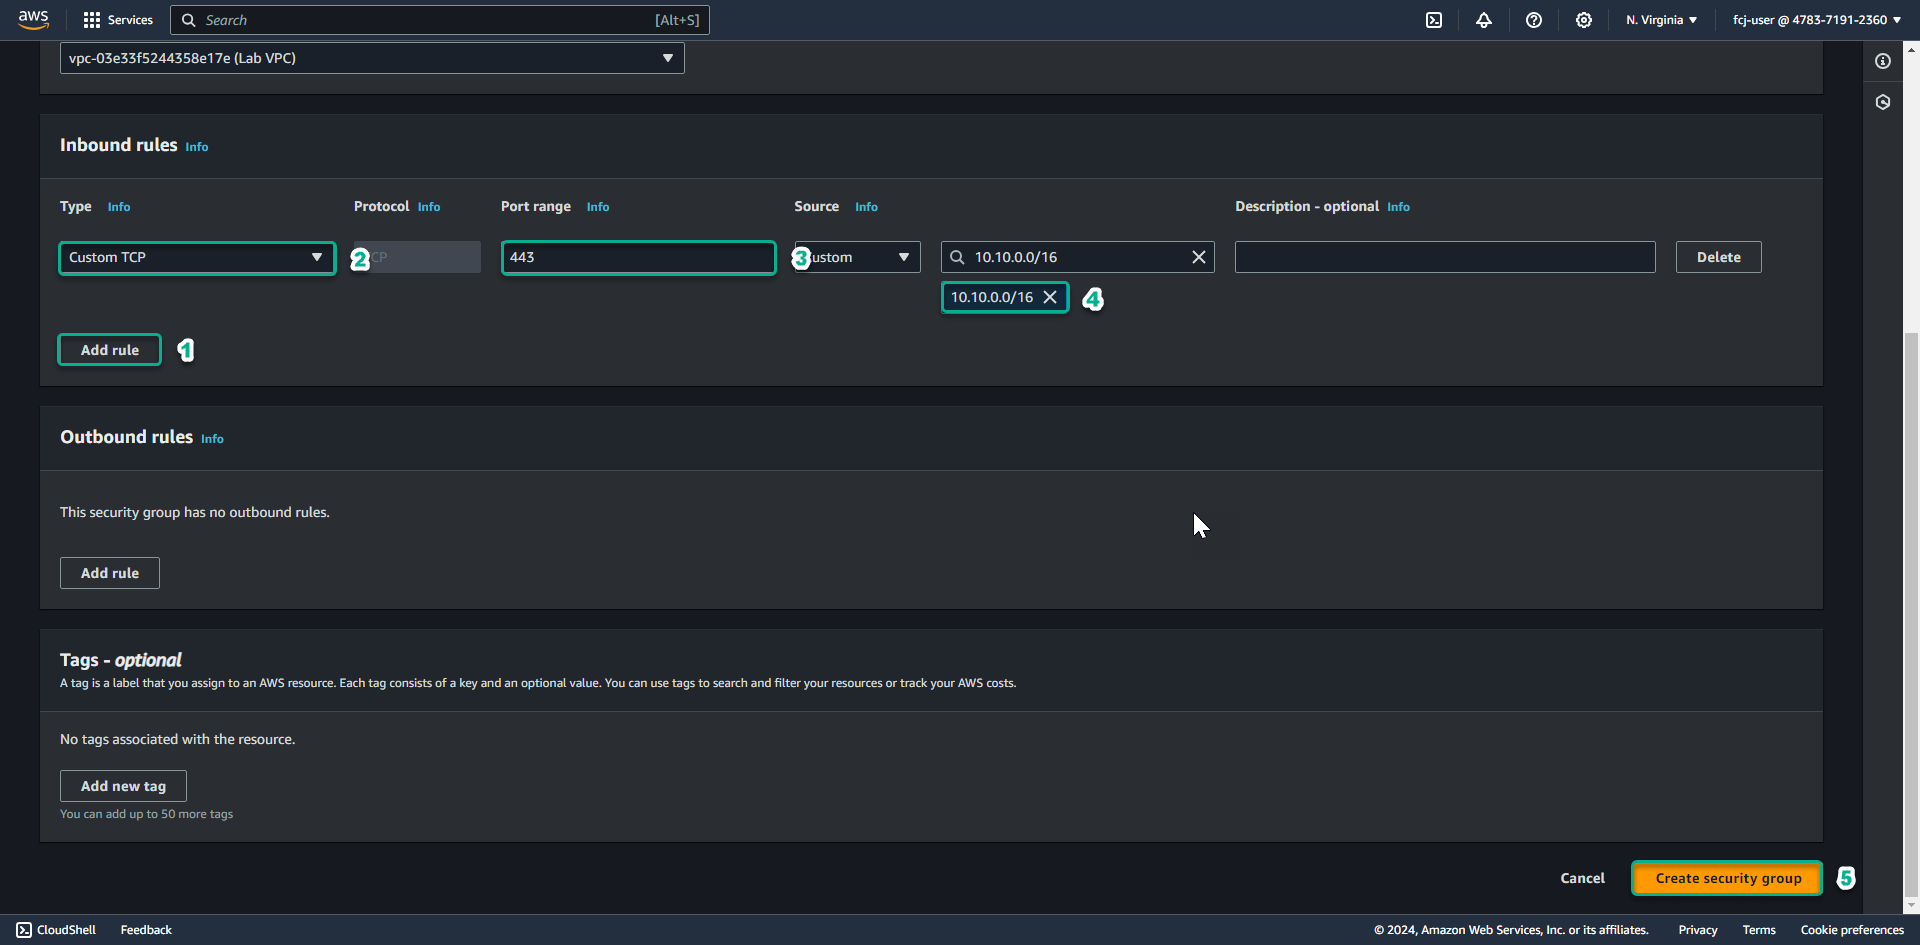
Add an Inbound rule to allow TCP 443 from 10.10.0.0/16 (CIDR of the Lab VPC we created).
- Click Create security group.
- Click Create security group.
Thus, we have finished creating the necessary security groups for the EC2 instances and VPC Endpoints.