Create IAM Role
Create IAM Role
In this step we will proceed to create an IAM Role. This IAM Role will be attached with the AmazonSSMManagedInstanceCore policy, which is a policy that allows the EC2 server to communicate with Session Manager.
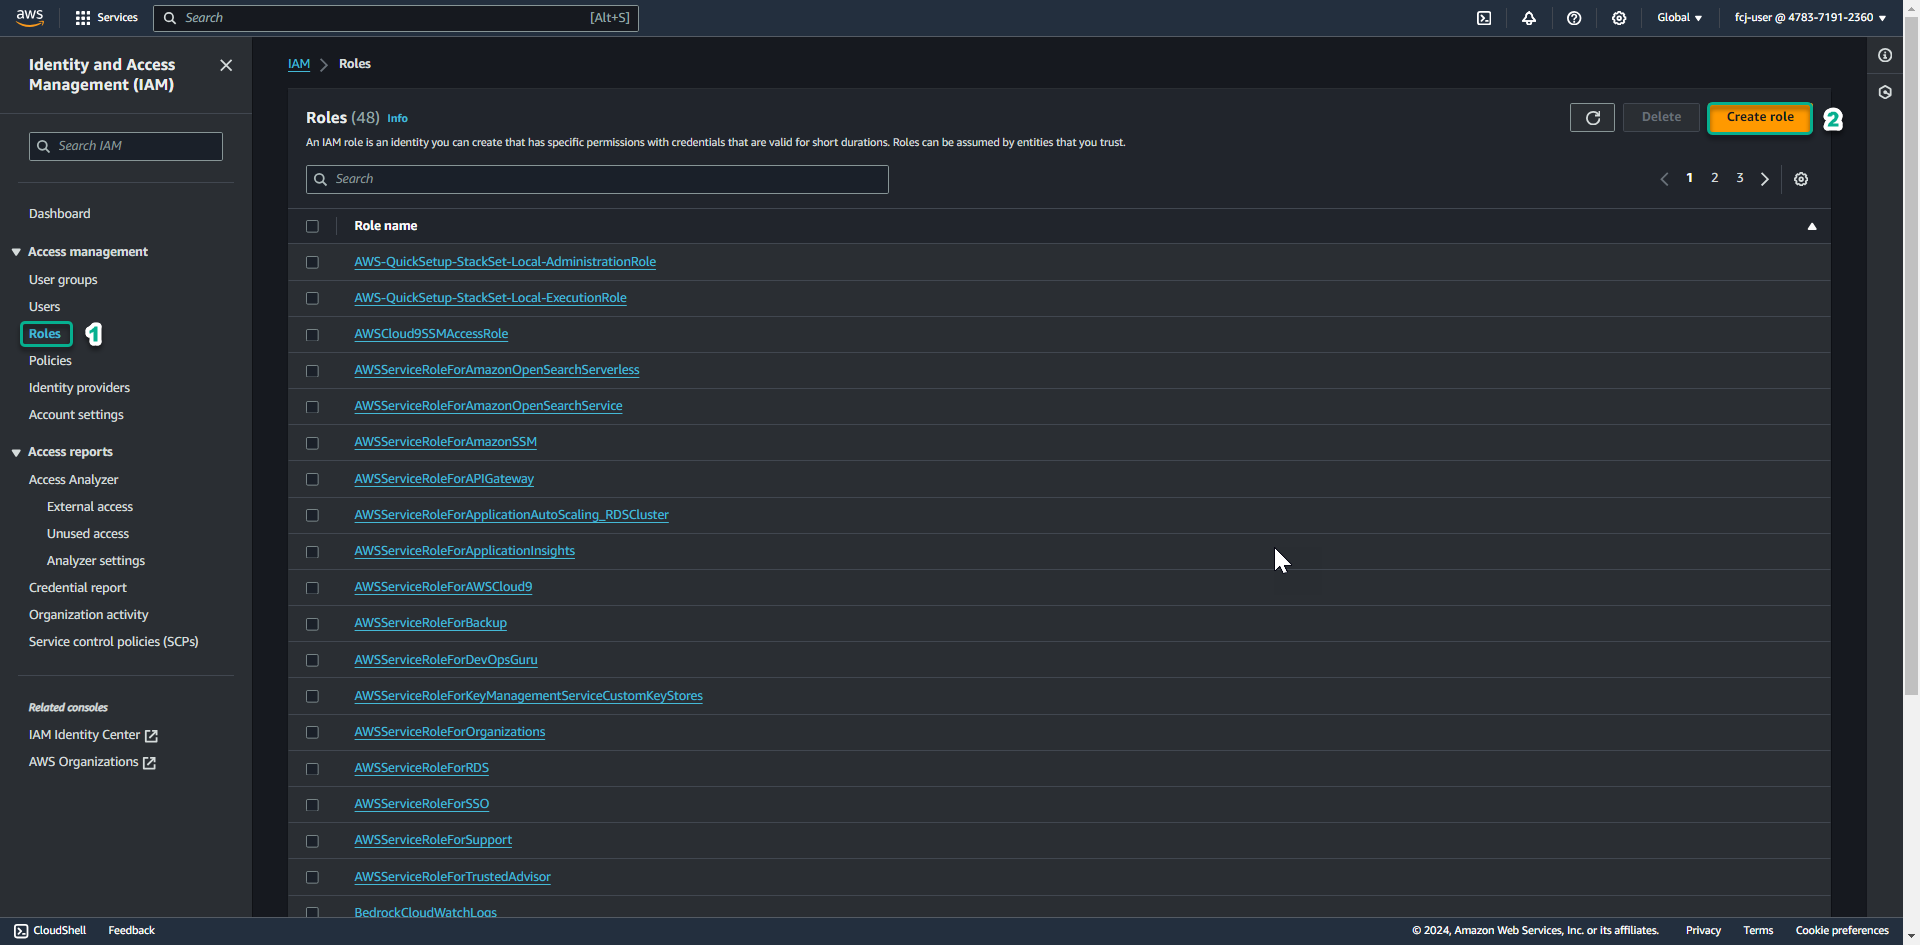
- Access the IAM service management console
- In the left navigation pane, click Roles.
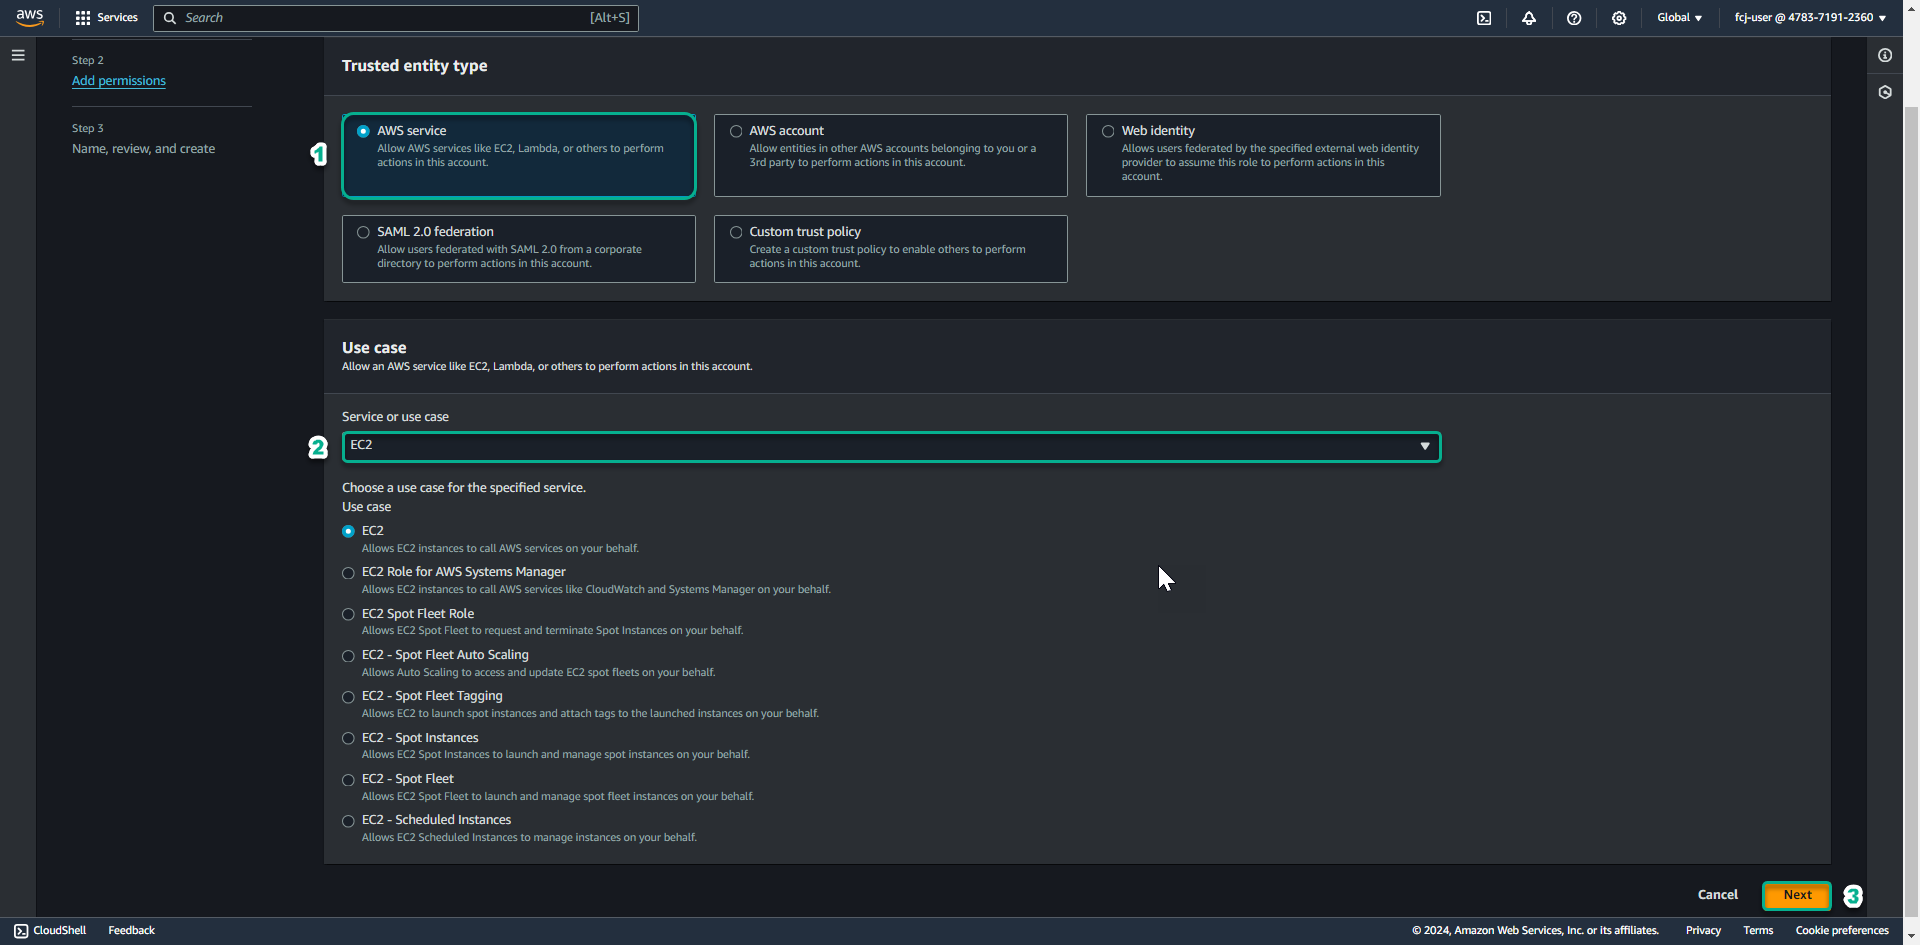
Select AWS service, then select EC2.
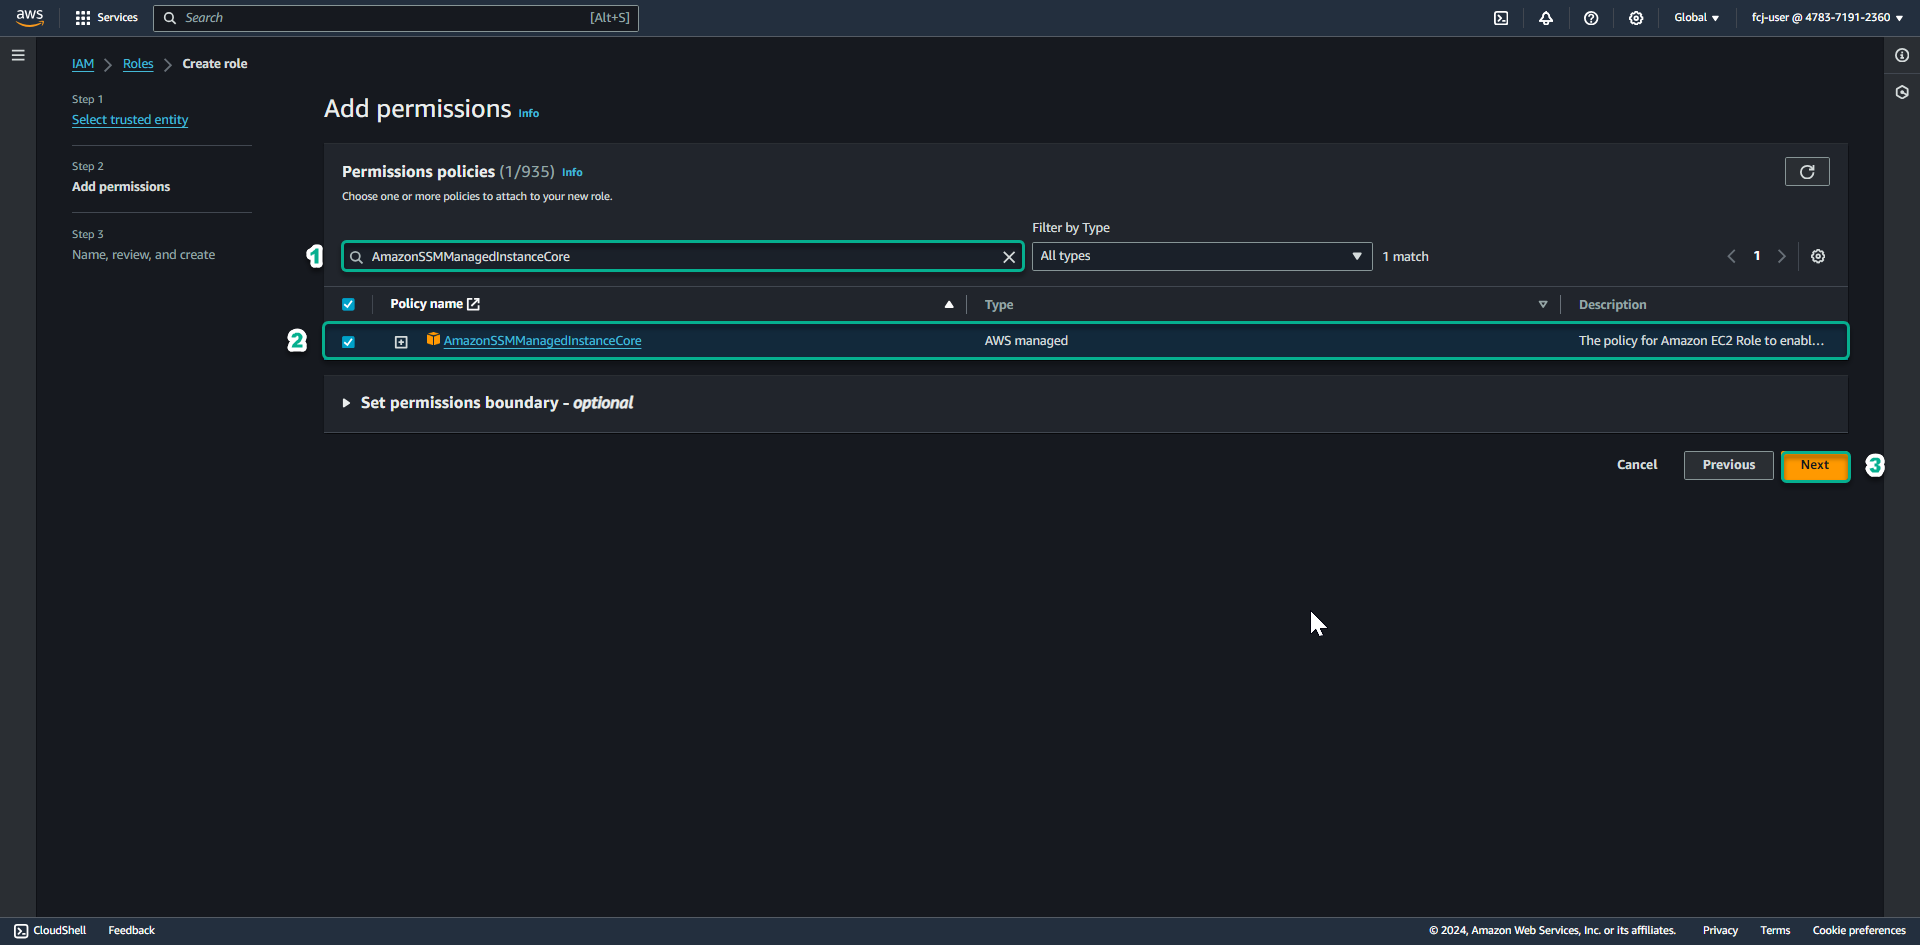
In the search bar, enter AmazonSSMManagedInstanceCore and press enter to search for this policy.
- Click policy AmazonSSMManagedInstanceCore.
- Click Next
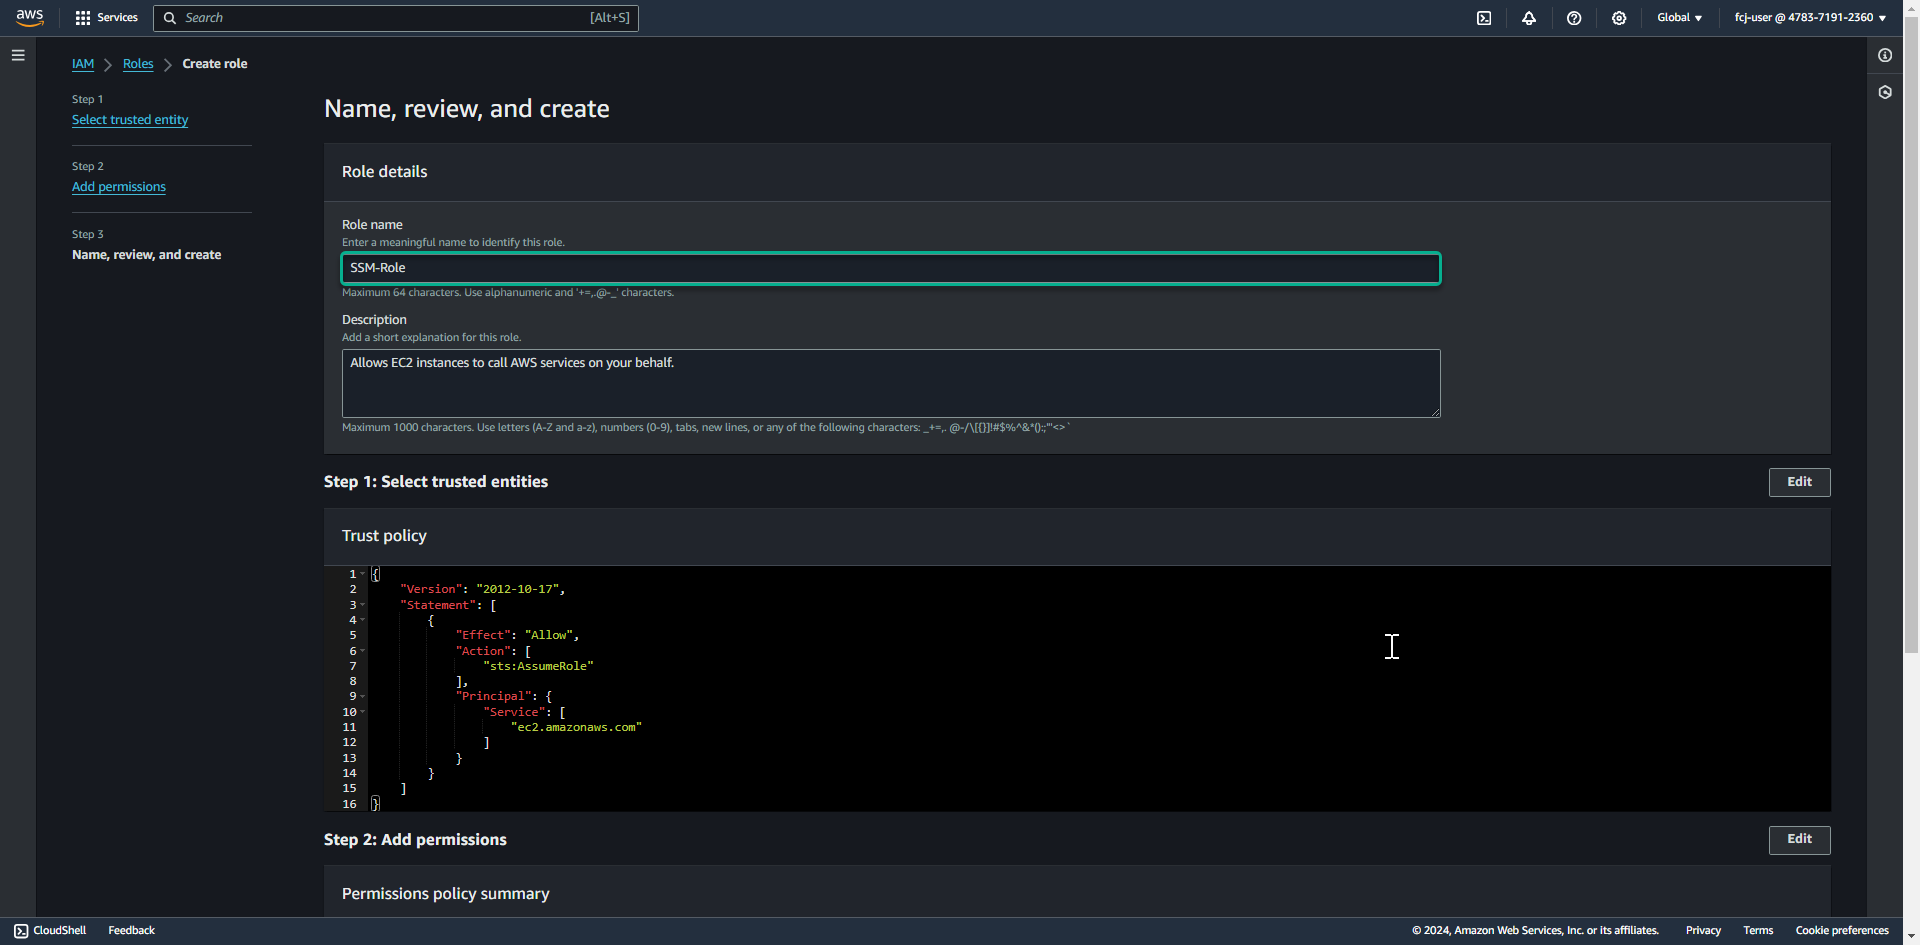
Name the role:
SSM-Role- Click Create Role.
- Click Create Role.
Next we will connect to the EC2 servers we have created using Session Manager.