Monitor session logs
Update Security Group
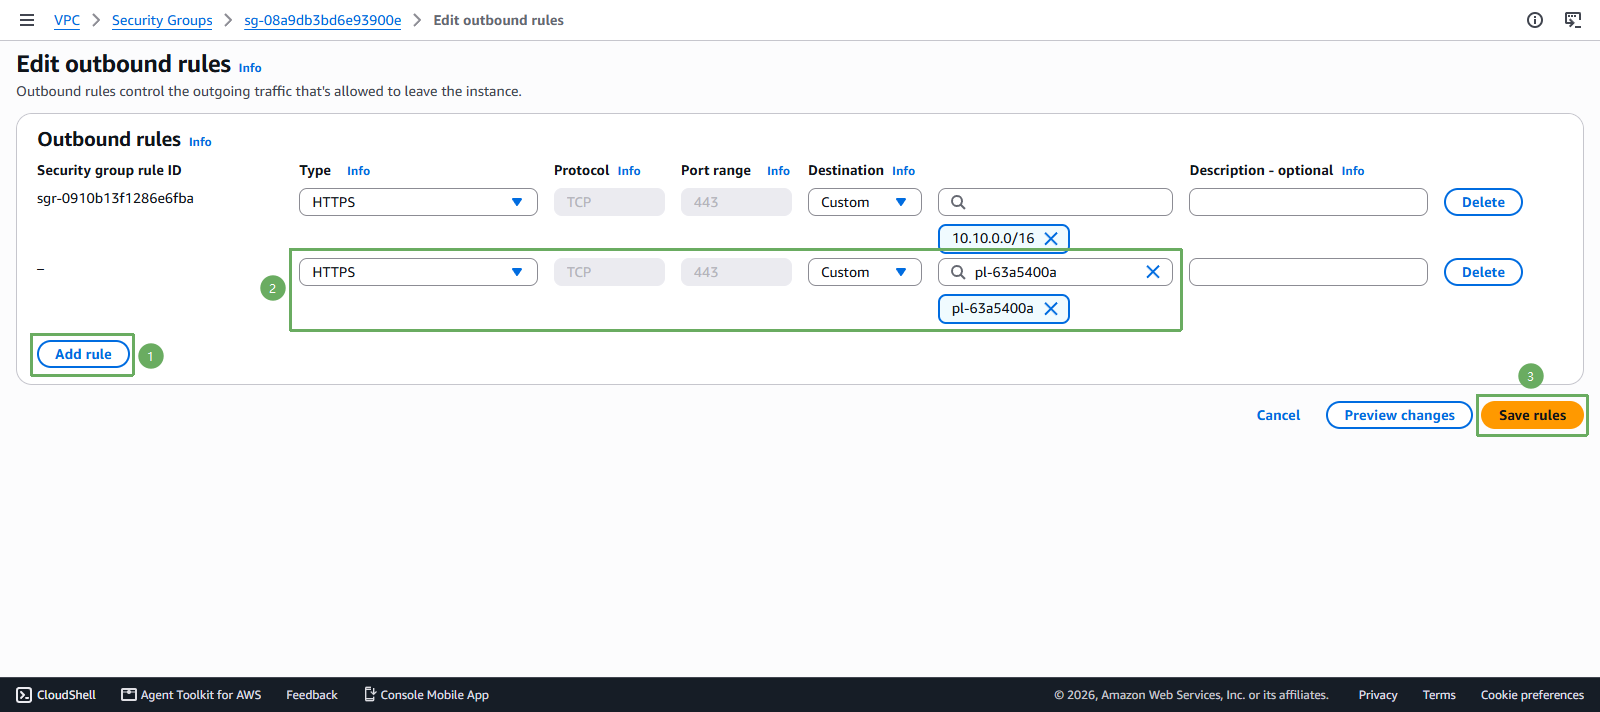
For the instance to be able to send logs to S3 through the S3 Gateway Endpoint, we need to allow outbound traffic to S3.
Access the VPC service management console
- Click Security Groups.
- Select SG Private Windows Instance.
- Select the Outbound rules tab and click Edit outbound rules.
Click Add rule:
- Type: HTTPS
- Destination: Select Custom, click in the search box, type
pl-and select the S3 prefix list (e.g.,com.amazonaws.us-east-1.s3). - Click Save rules.
Configure session logs storage
Access the Systems Manager - Session Manager service console
- Click the Preferences tab.
- Click Edit.

Scroll down, in the S3 logging section,
- Click select Enable for Send session logs to S3.
- Select Allow only encrypted S3 buckets.
- Click select Choose a bucket name from the list.
- Select the S3 bucket you created.

Scroll down, click Save to save the configuration.
Access the Systems Manager - Session Manager service console
- Click Start session.
- Click select Private Windows Instance.
- Click Start session.
Type the ipconfig command.
- Type the hostname command.
- Click Terminate to exit the session, click Terminate once more to confirm.

Check Session logs in S3
Access the S3 service management console
- Click on the name of the S3 bucket we created for the lab.
Click on the session log file name

At the object details page, click Open.

The log file will be opened in a new tab in the browser. You can view the commands that have been stored in the session logs.
