Update IAM Role
For our EC2 instances to be able to send session logs to an S3 bucket, we will need to update the IAM Role attached to the EC2 instances by adding a policy that allows access permissions to S3.
Update IAM Role
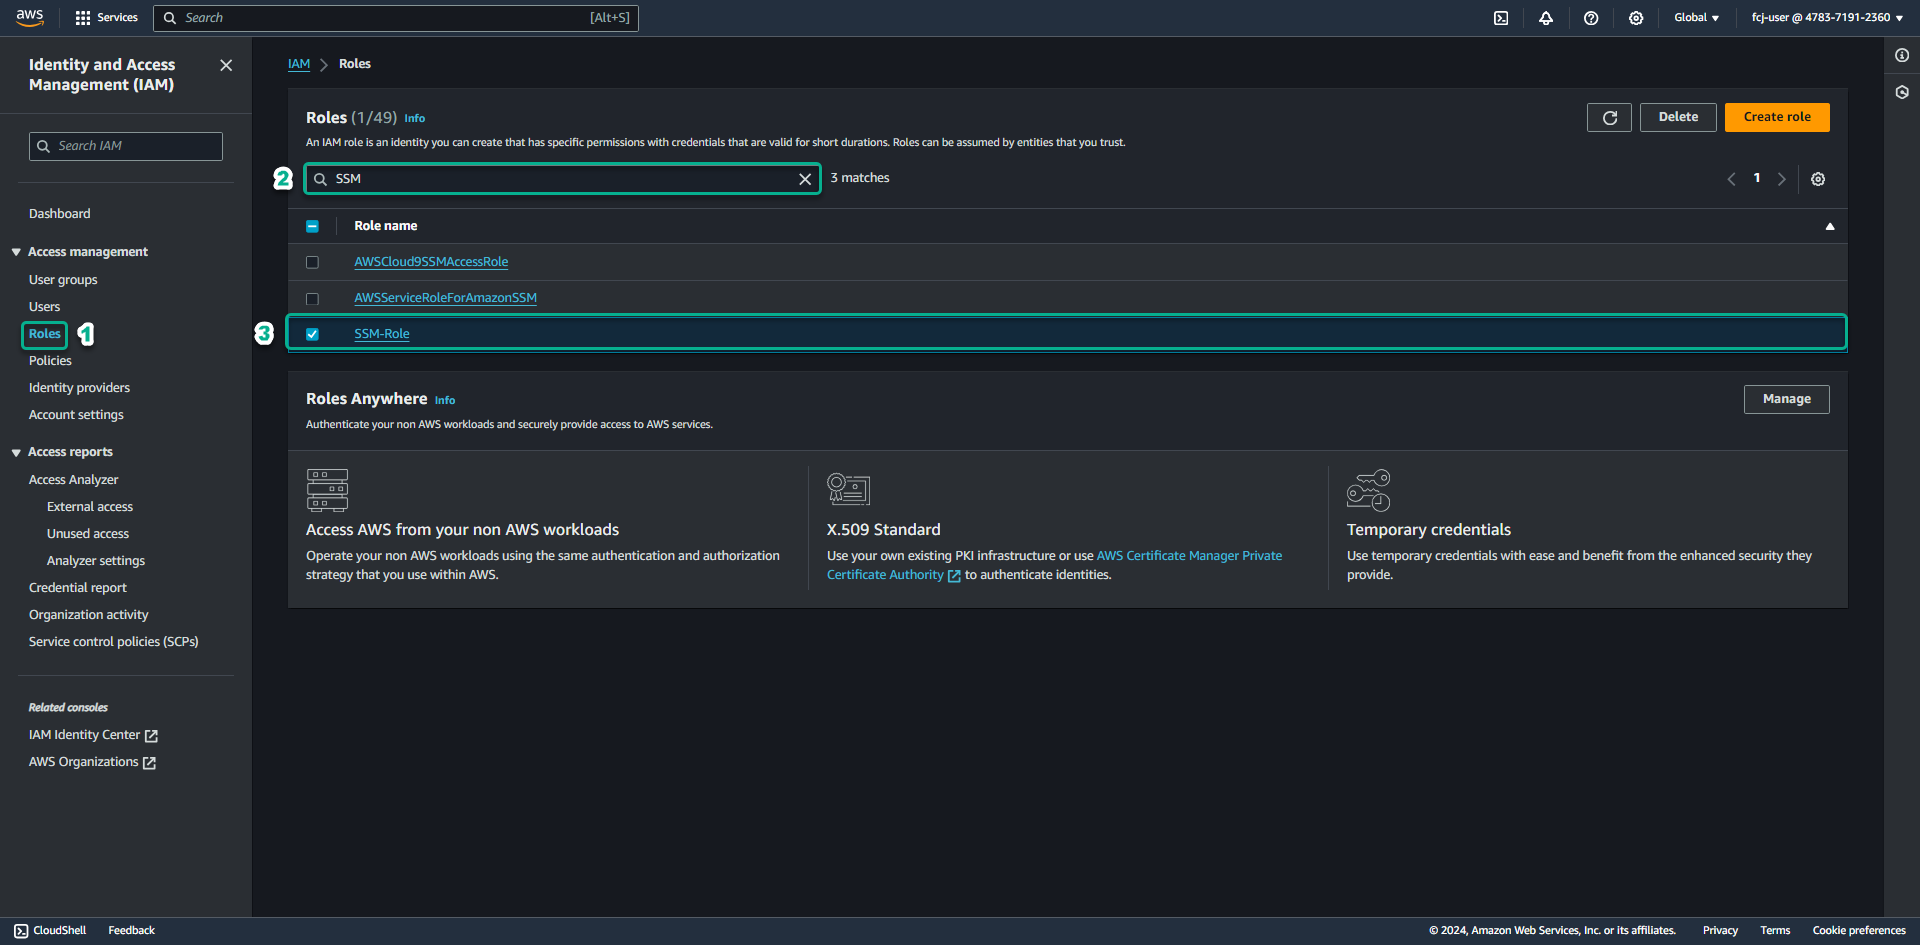
Access the IAM service management console
- Click Roles.
- In the search box, enter SSM.
- Click on the SSM-Role role.
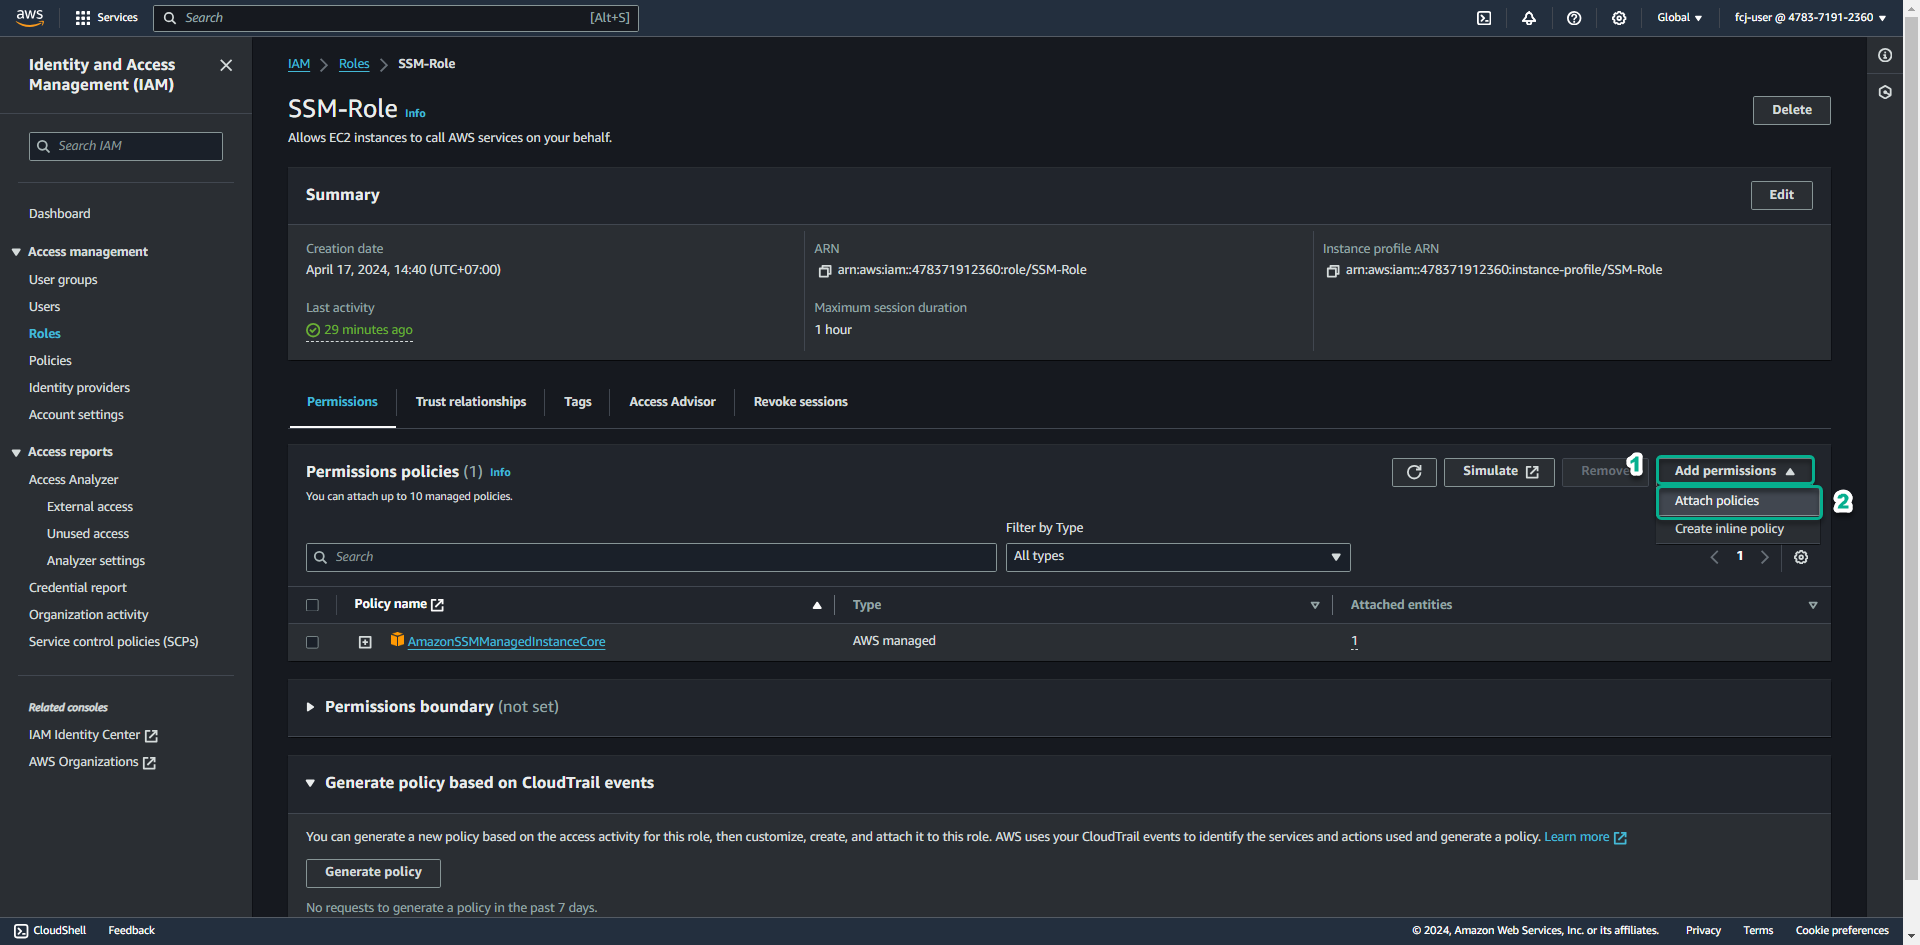
Click Attach policies.
In the Search box enter AmazonS3FullAccess.
- Click select the AmazonS3FullAccess policy.
- Click Add permissions.
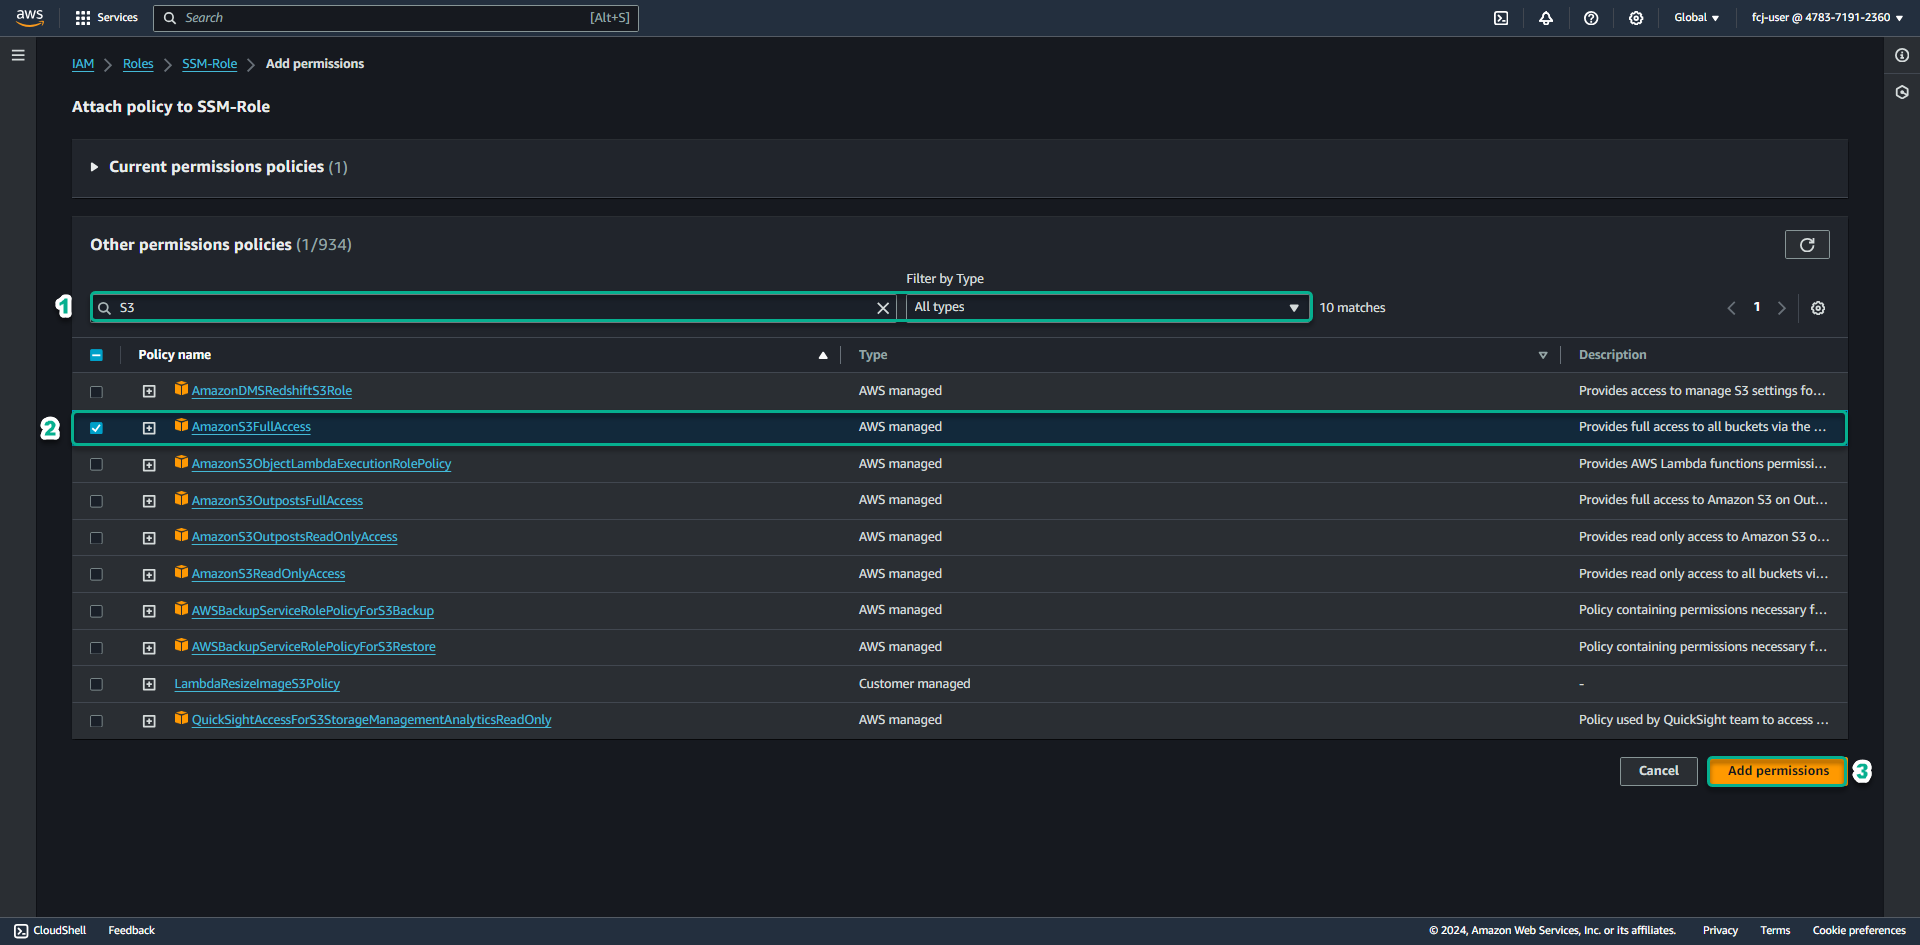
In practice we will grant stricter permissions to the specified S3 bucket. Within the scope of this lab we use the AmazonS3FullAccess policy for convenience.
Next we will proceed to create an S3 bucket to store session logs.