Connect to Public instance
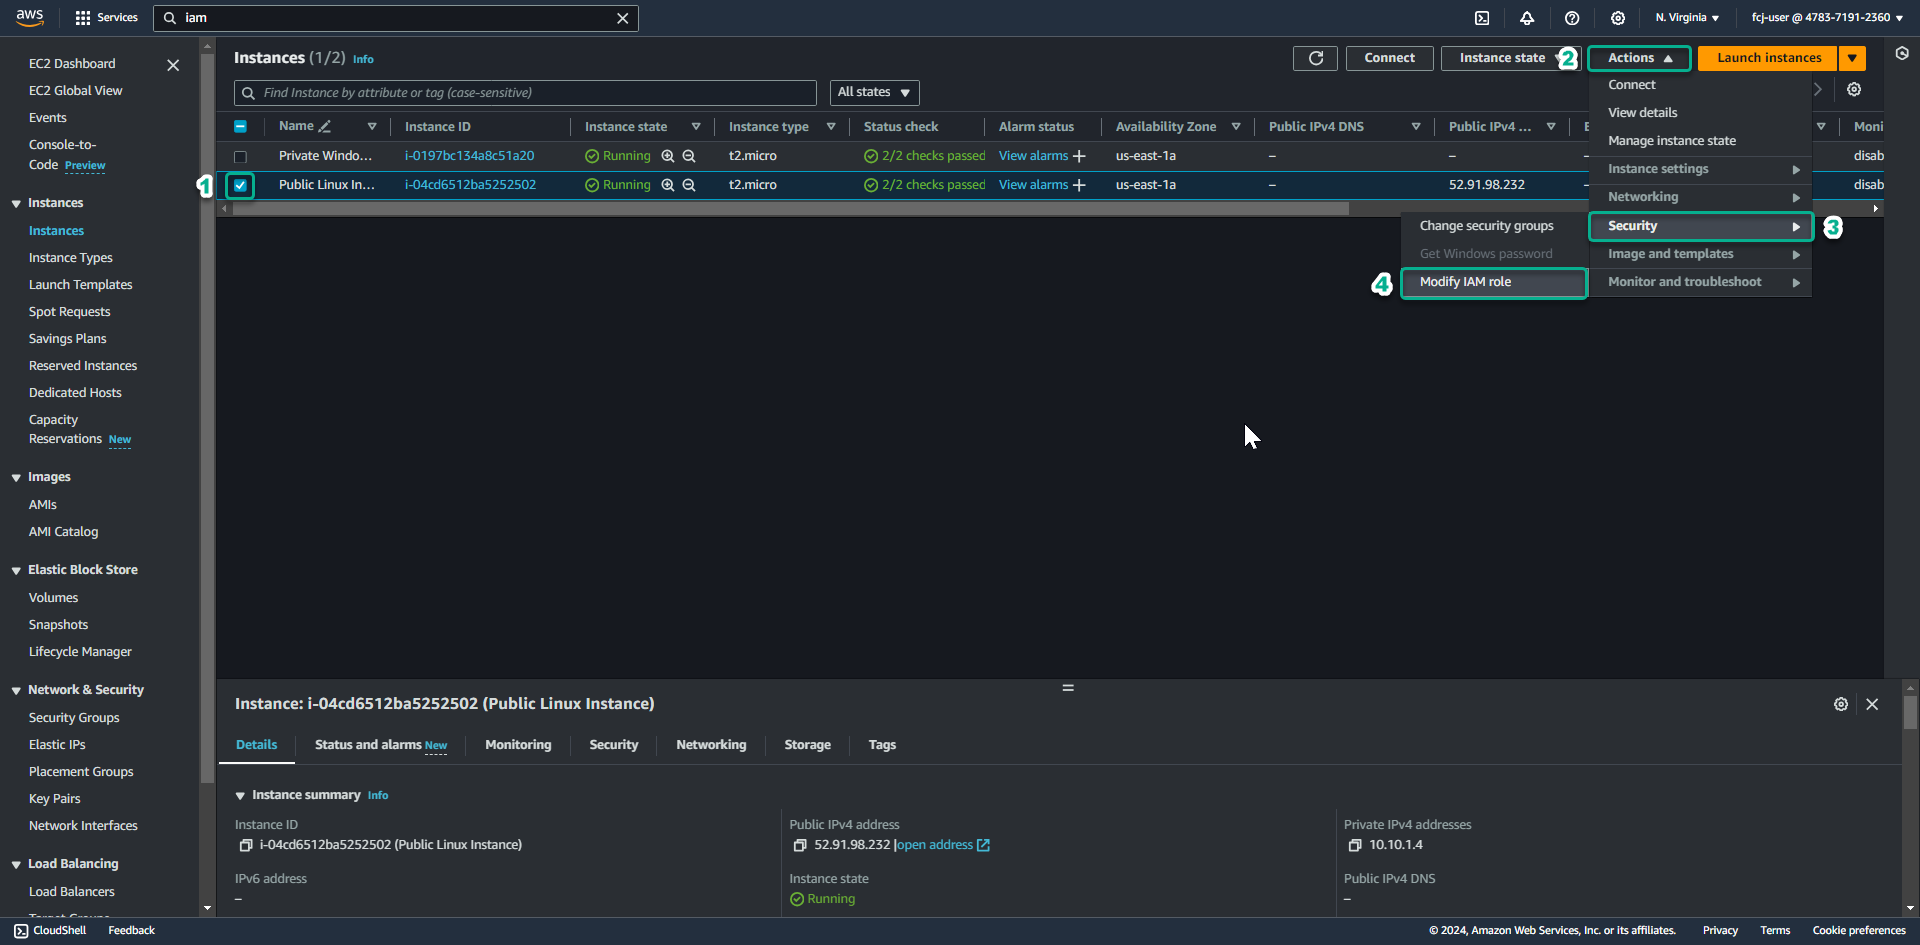
Access the EC2 service management console.
- Click select Public Linux Instance.
- Click Actions.
- Click Security.
- Click Modify IAM role.
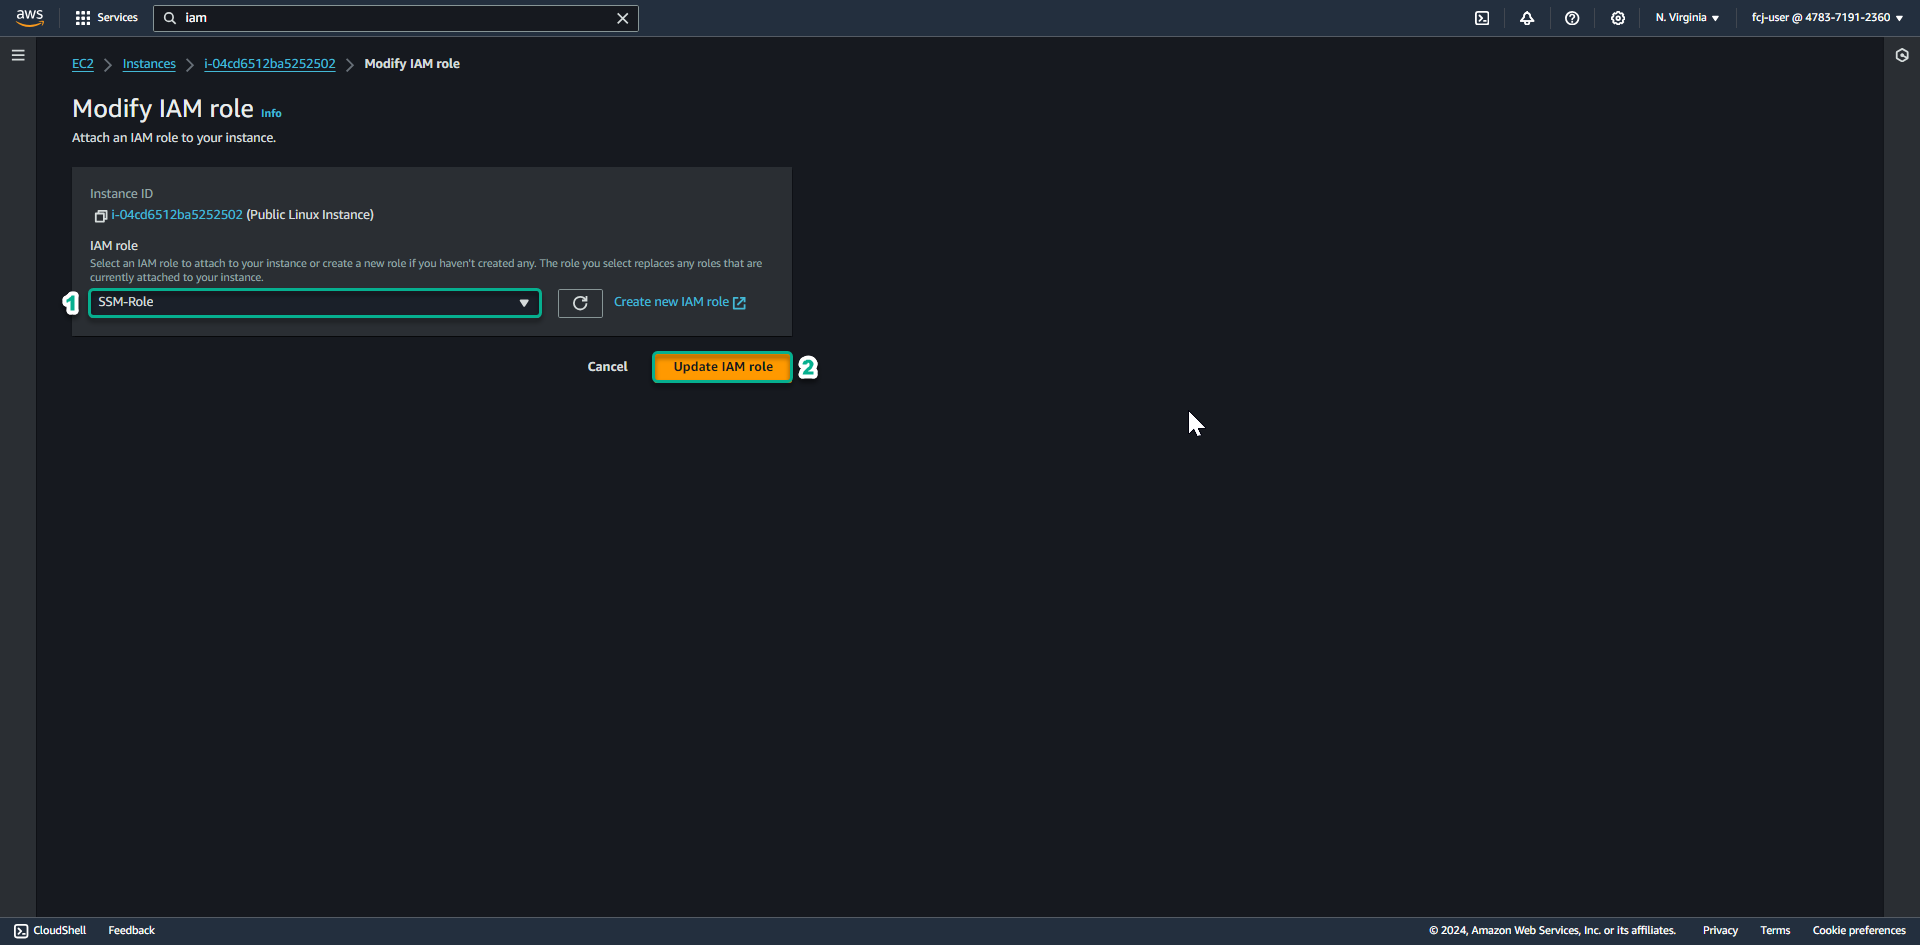
At the Modify IAM role page.
- Click select SSM-Role.
- Click Update IAM role.
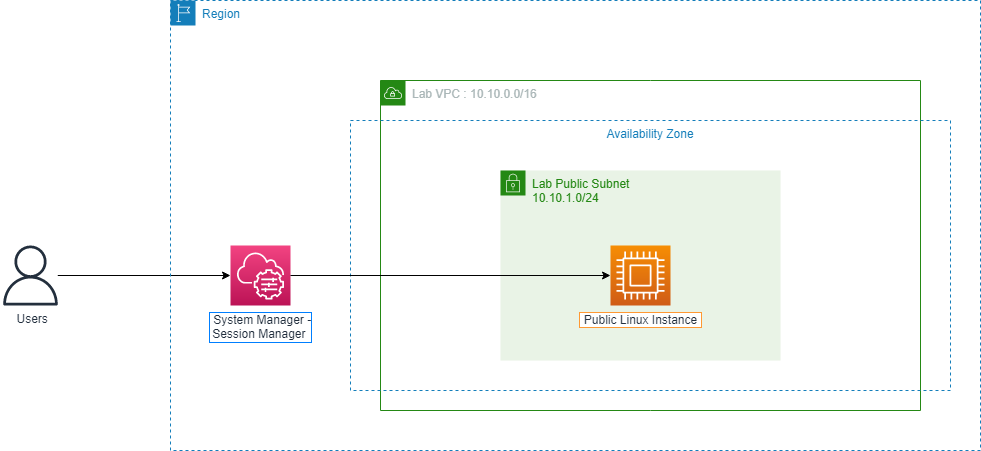
You will need to wait about 10 minutes before proceeding to the next step. During this time our EC2 instance will automatically register with Session Manager.
Access the AWS Systems Manager service console
- Scroll down the left menu slider.
- Click Session Manager.
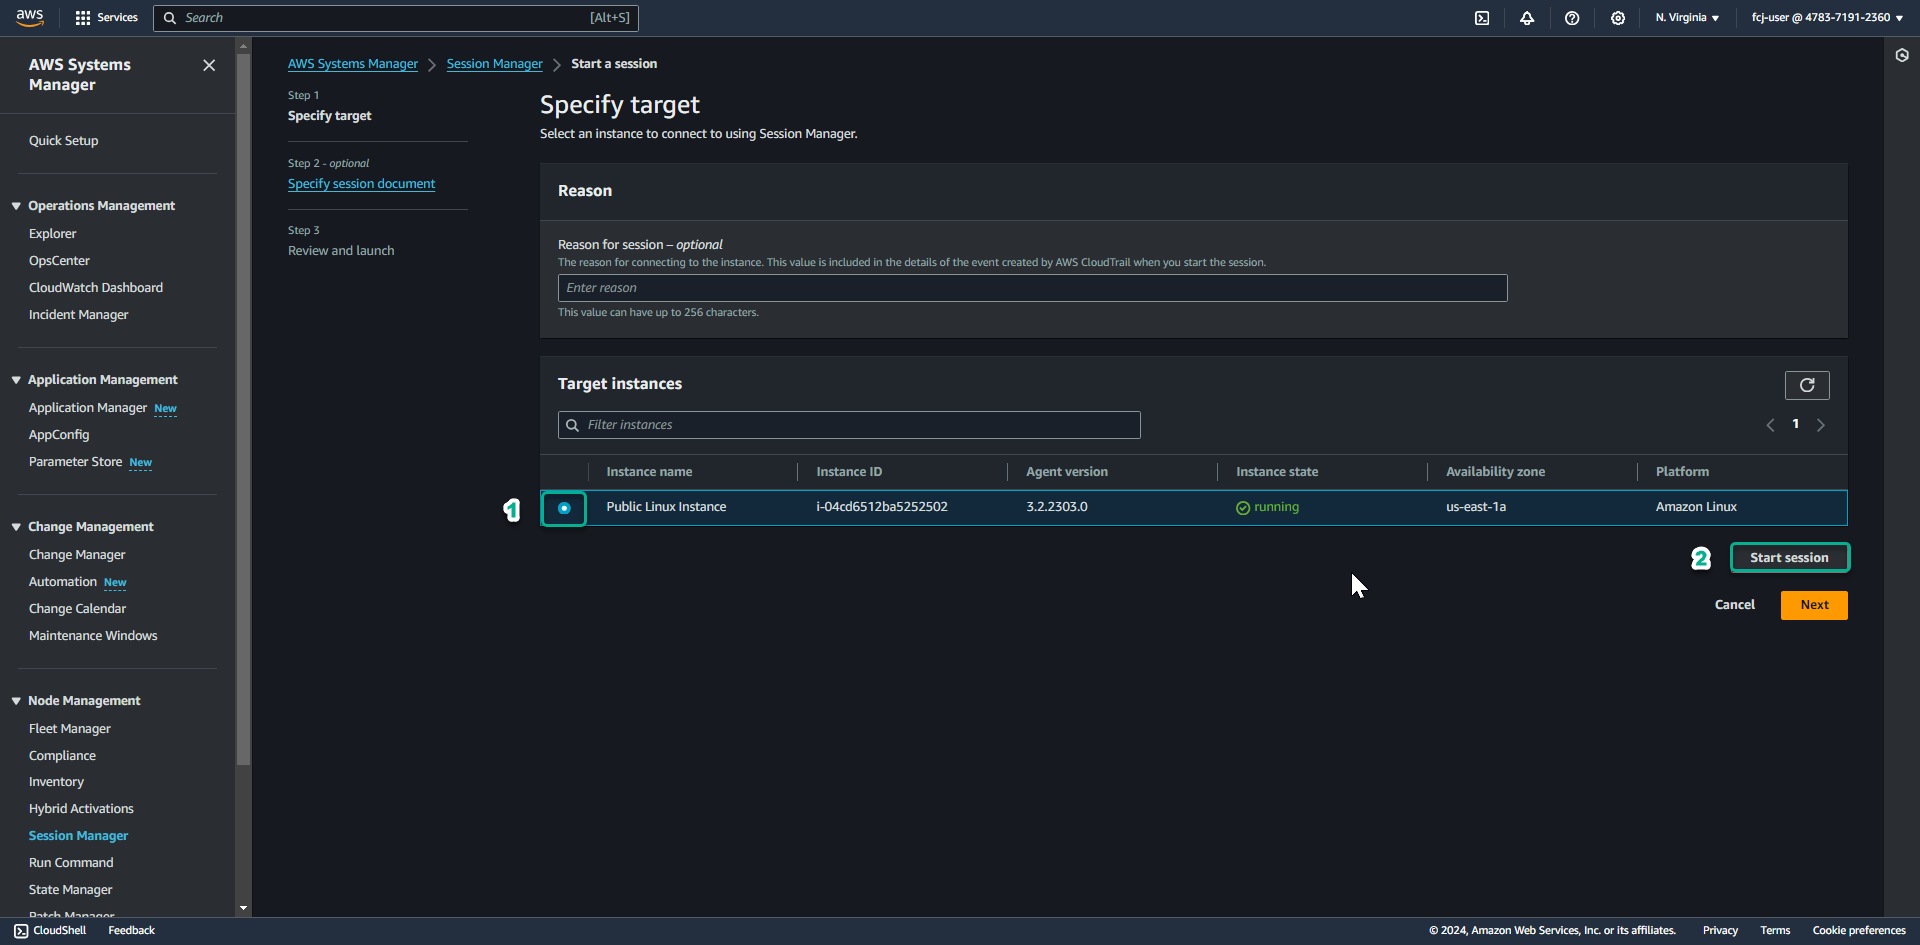
- Click Start Session.
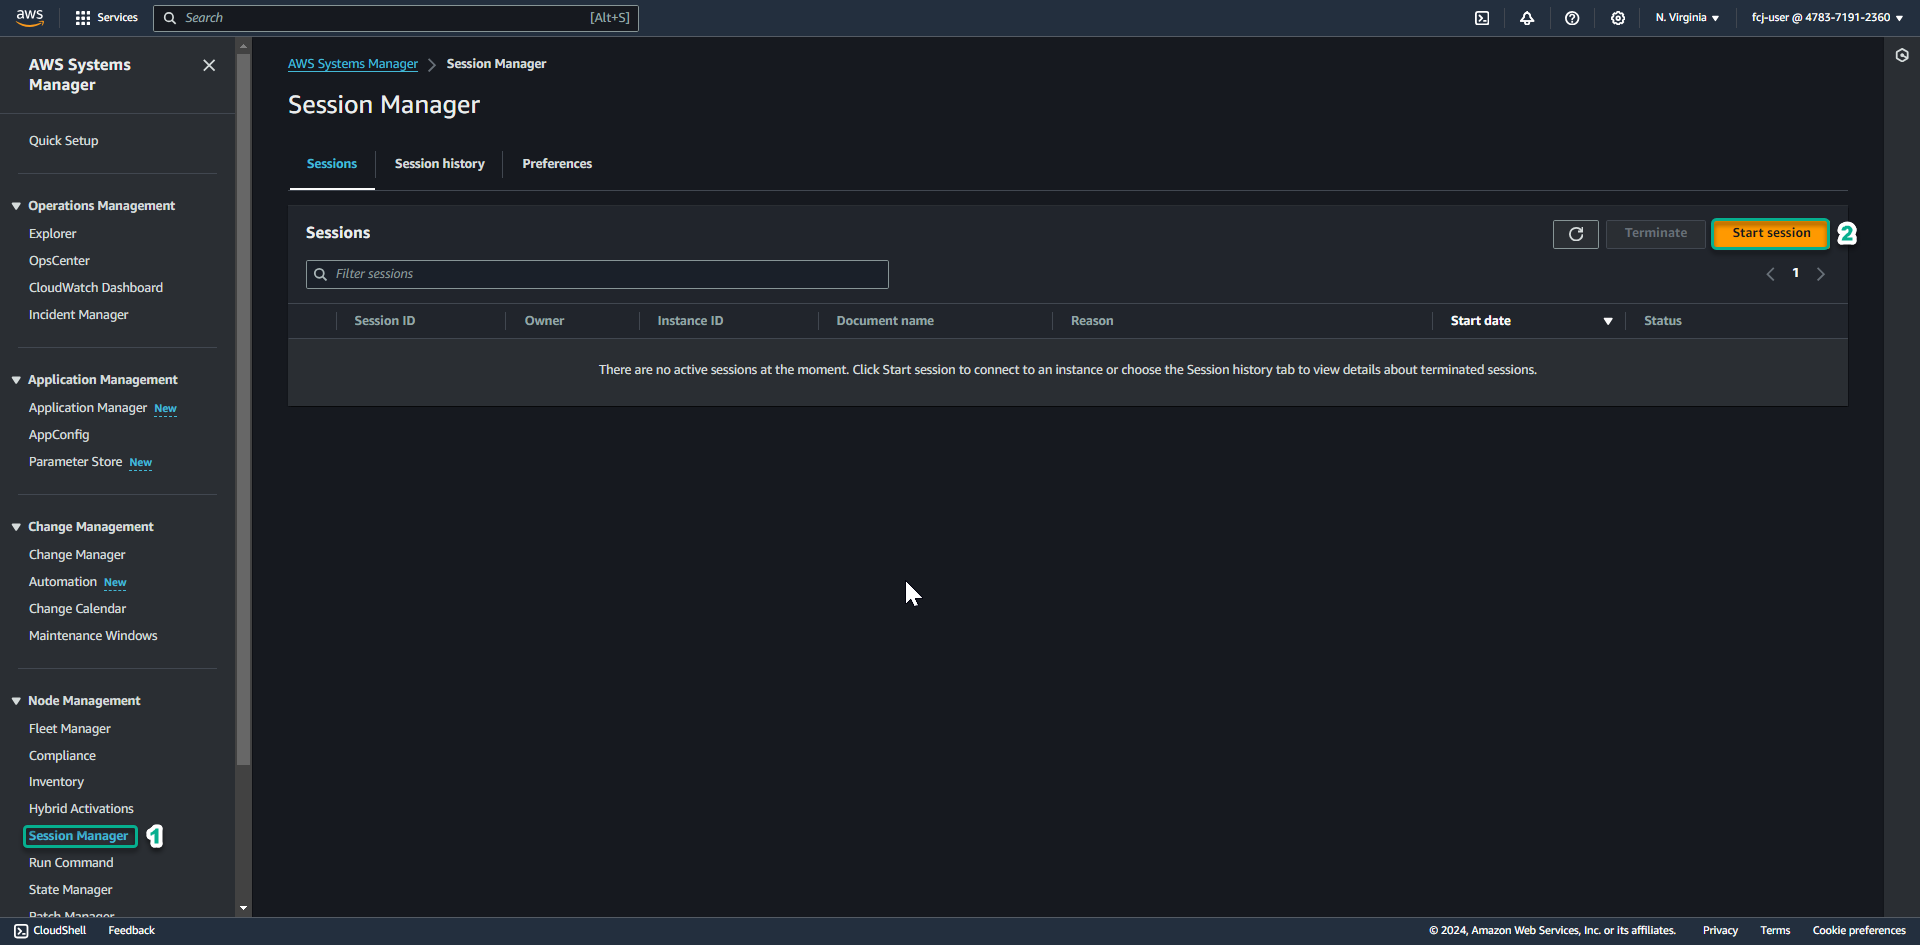
Then select Public Linux Instance and click Start session to access the instance.
The terminal will appear on the browser. Check with the command
sudo tcpdump -nn port 22andsudo tcpdumpwe will see no SSH traffic but only HTTPS traffic.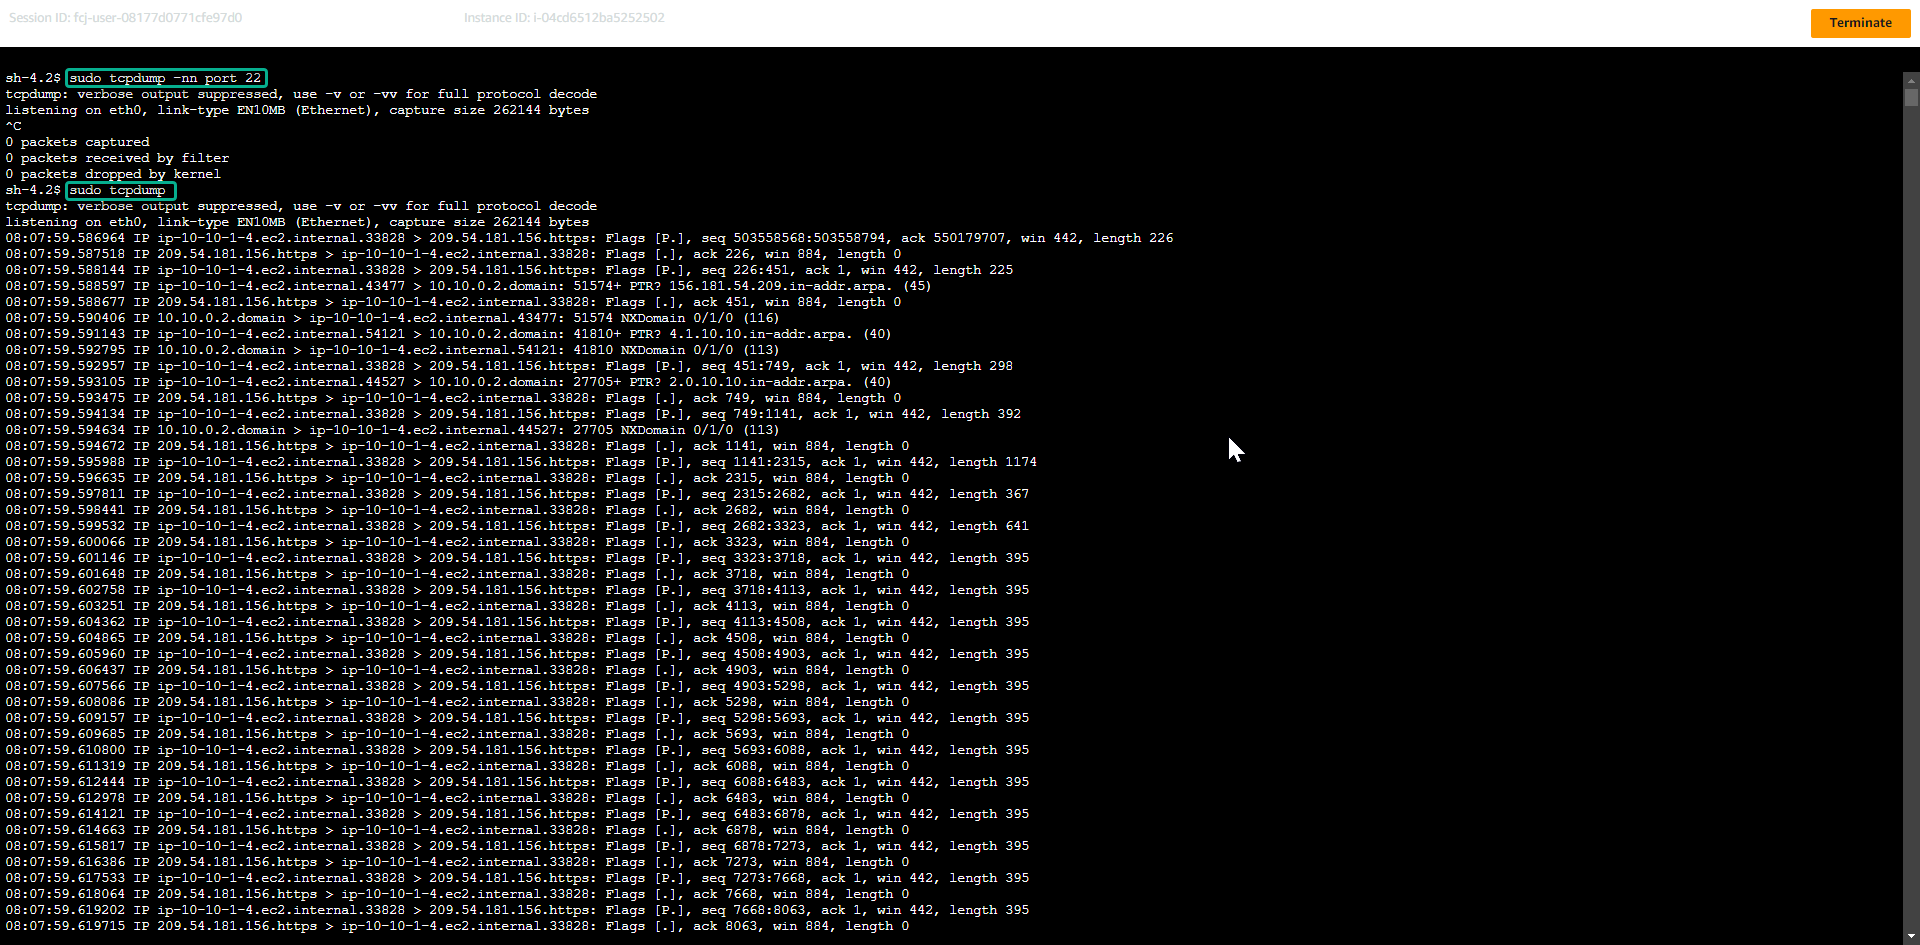
Above, we created a connection to the public instance without having to open SSH port 22, helping for better security, avoiding any attacks to the SSH port.
A disadvantage of the above approach is that we have to open the Security Group outbound at port 443 to the internet. Because it is a public instance, there may be no problem, but if you want to be more secure, you can lock port 443 to the internet and still use Session Manager. We will go through this approach in the private instance section below.
You can terminate to end the connecting session before going to the next step.